> For the complete documentation index, see [llms.txt](https://knowledge.whiteintel.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://knowledge.whiteintel.io/whiteintel-usage/investigations+-beta.md).
# Investigations+ (Beta)
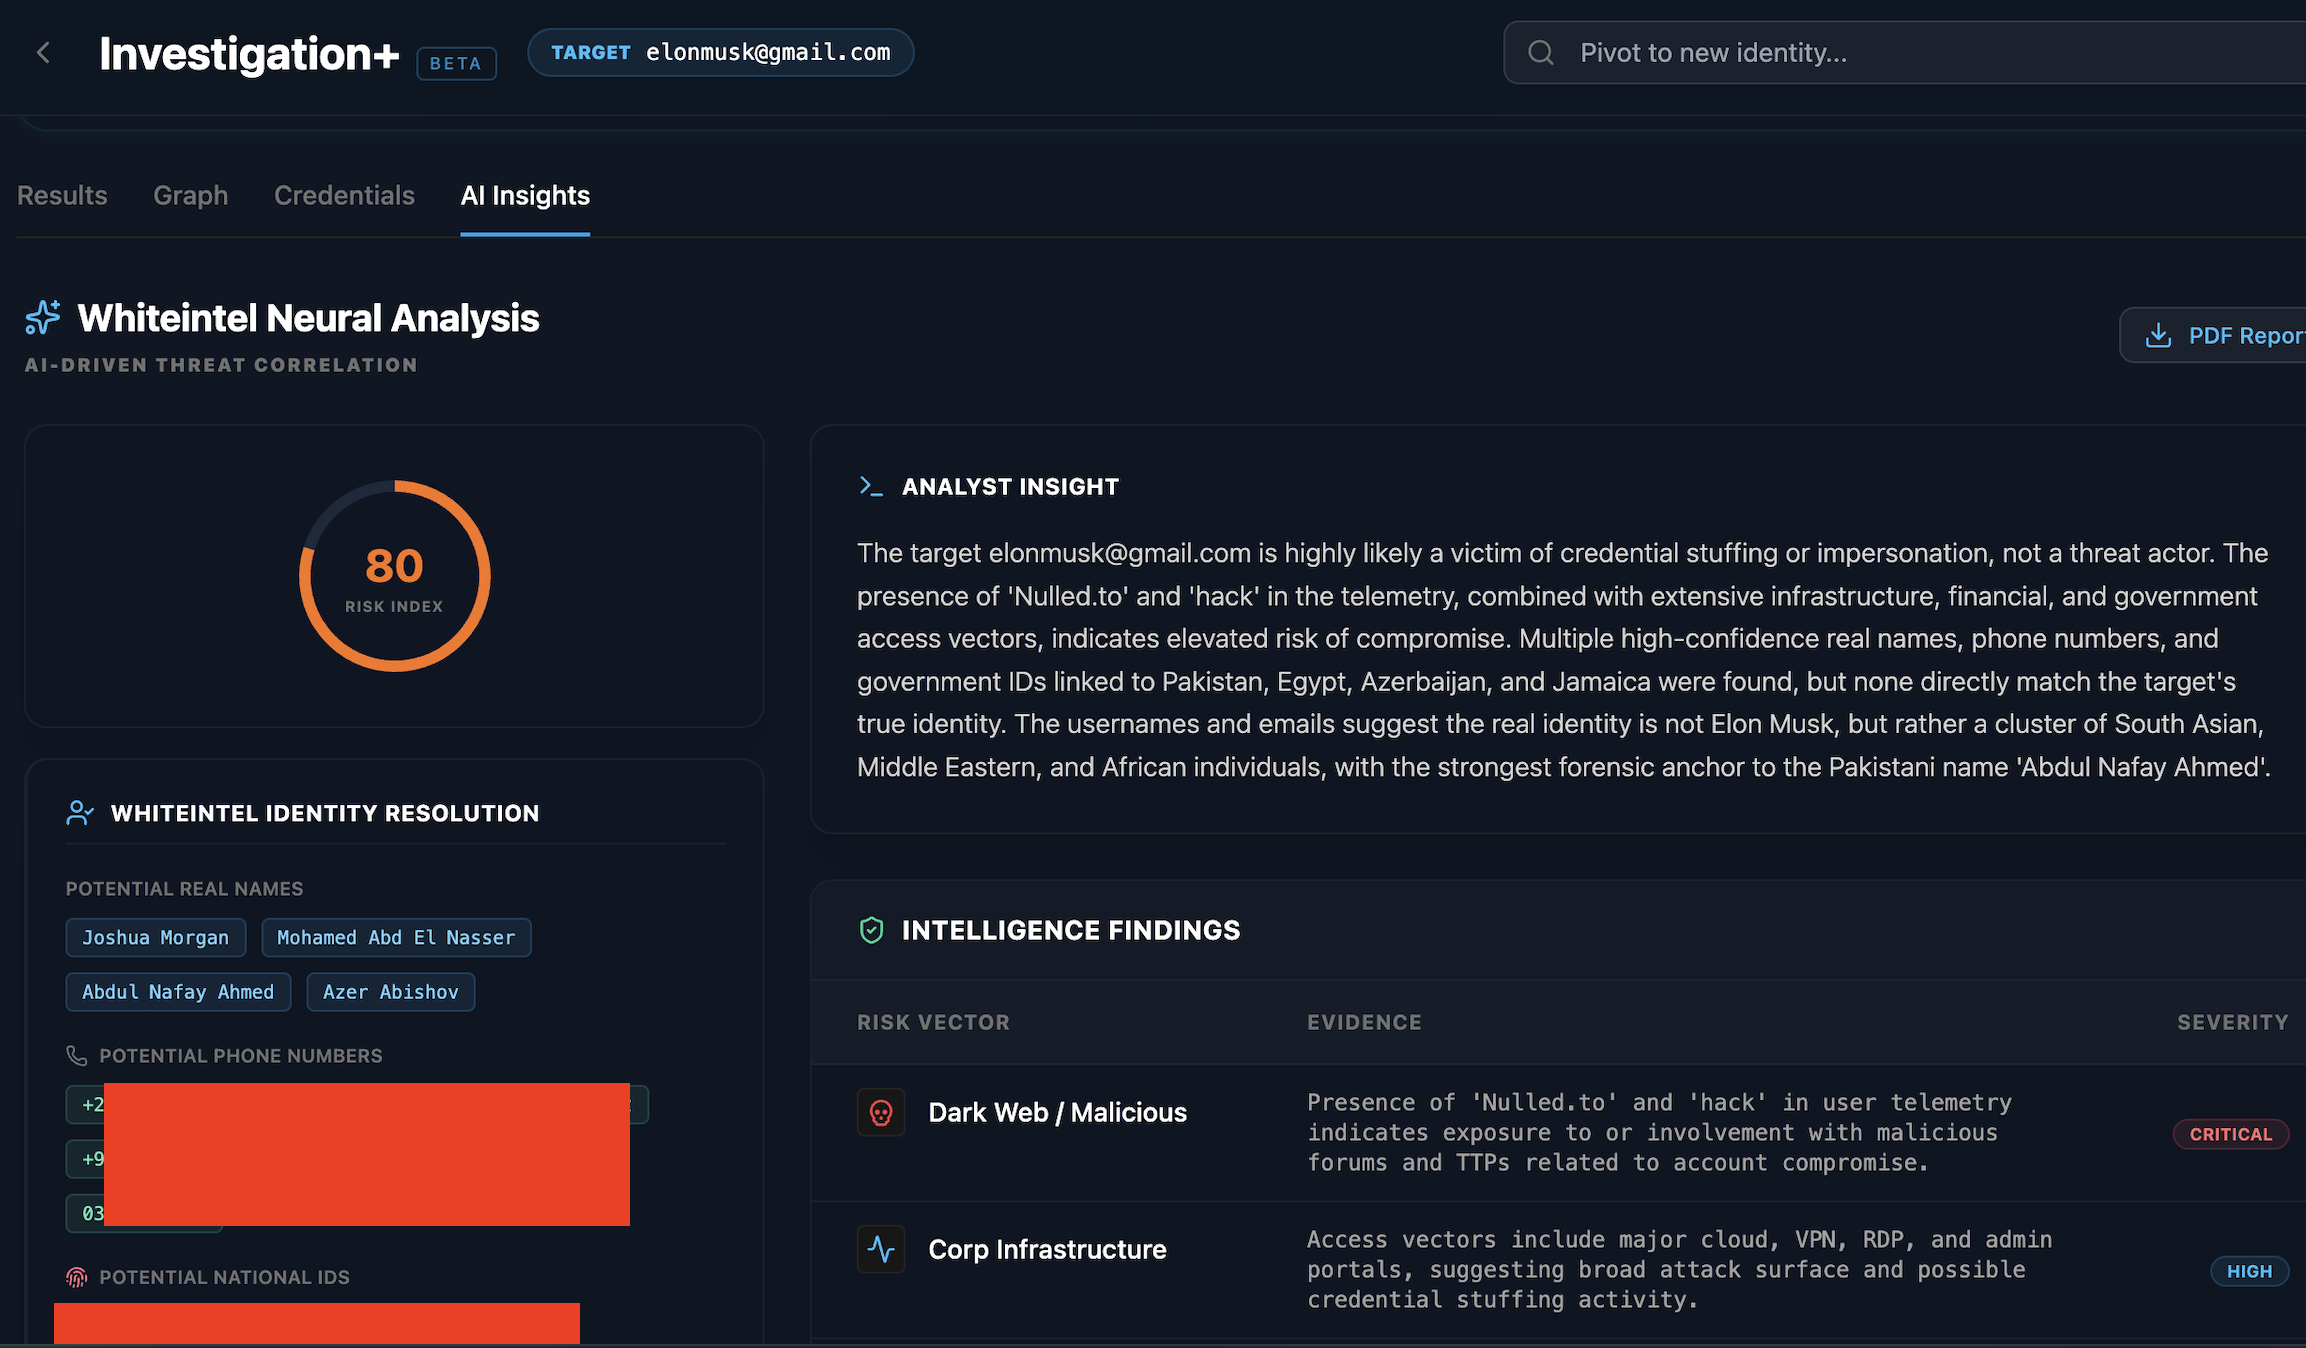
Investigation+ is WhiteIntel’s premium forensic suite, designed to transform raw log data into actionable intelligence. By leveraging neural correlation and autonomous heuristics, this module allows analysts to de-anonymize targets, visualize lateral exposure, and prioritize critical assets through a centralized dashboard experience.
> ⚠️ Platform Availability: This module is accessible exclusively through the WhiteIntel Web Dashboard. To protect the integrity of our identity graph and the compute-heavy neural models involved, this feature is not available via the API.
### 🚀 Core Capabilities
The Investigation+ module is built around four pillars of forensic discovery:
## 1. Comprehensive Assets Discovery
The Investigation+ module provides a comprehensive inventory of all known assets connected to the target username or email. This view consolidates fragmented log data into a unified forensic profile.
### 1.1. Connected Assets
The engine aggregates and displays:
* Computer Names: Hostnames of every infected machine linked to the target.
* IP Addresses: History of connection points and network origins.
* Observed Countries: Geographic anchoring based on IP telemetry and TLD analysis.
* Related Accounts: Secondary usernames, aliases, and emails used by the same individual.
* Passwords: A curated list of observed passwords, useful for identifying credential reuse patterns.
#### 1.2. Application Intelligence
The Results Tab also features a Detailed List of Affected Applications, showing every service, portal, or software package where the target's credentials have been captured.
## 2. Neural Identity Resolution
The engine performs linguistic forensics across thousands of data points to extract real-world identities from digital aliases.
* Cultural Anchoring: Matches surname patterns with detected geographic anchors (e.g., matching Pinyin names with `.gov.cn` assets).
* Cross-Log Correlation: Aggregates identifiers from multiple infected systems to build a single "Primary Identity" profile.
## 3. Forensic Graph Reconstruction
Visualize how a threat actor or target moves across a network. The graph maps the relationship between Infected Systems, Related Accounts, and Applications.
* Interactive Expansion: Click nodes to perform "Deep Dives" into secondary pivots.
* Application Nodes: Identify specific services where credentials were exfiltrated.
## 4. Smart Credential Prioritization
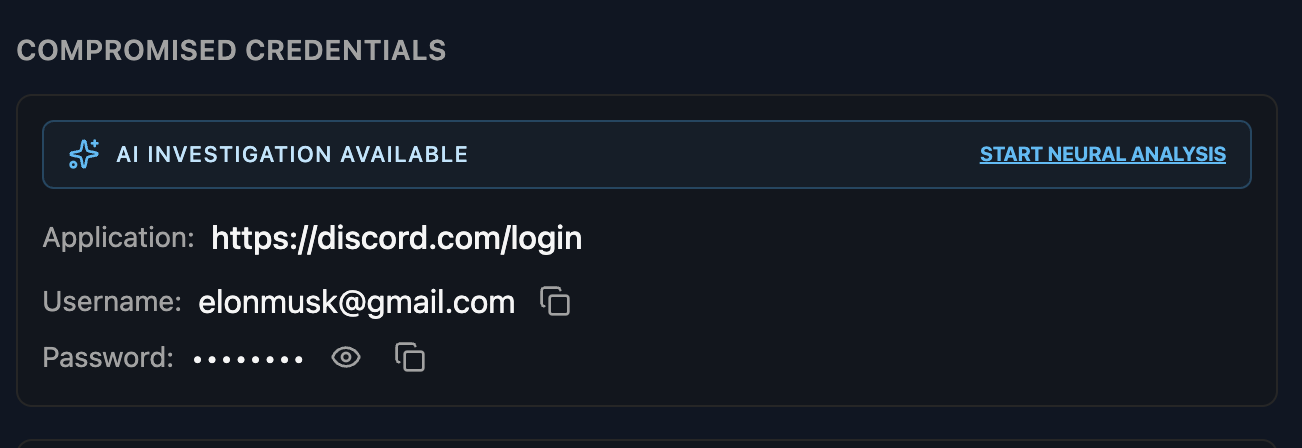
Instead of manually sorting through thousands of rows, the system automatically flags credentials based on their institutional value.
* High-Value Tags: Automatic categorization of Gov, Edu, and Malicious (Underground Forum) logins.
* Risk Context: Prioritizes administrative access and internal infrastructure portals.
## 5. Automated Risk Scoring
Every investigation is assigned a Risk Index based on the severity of the exposed data.
* Critical: Access to Government infrastructure or active presence on Tier-1 malicious forums.
* Elevated: Access to corporate VPNs, Cloud management panels, or financial portals.
### 🛠 Using the Module
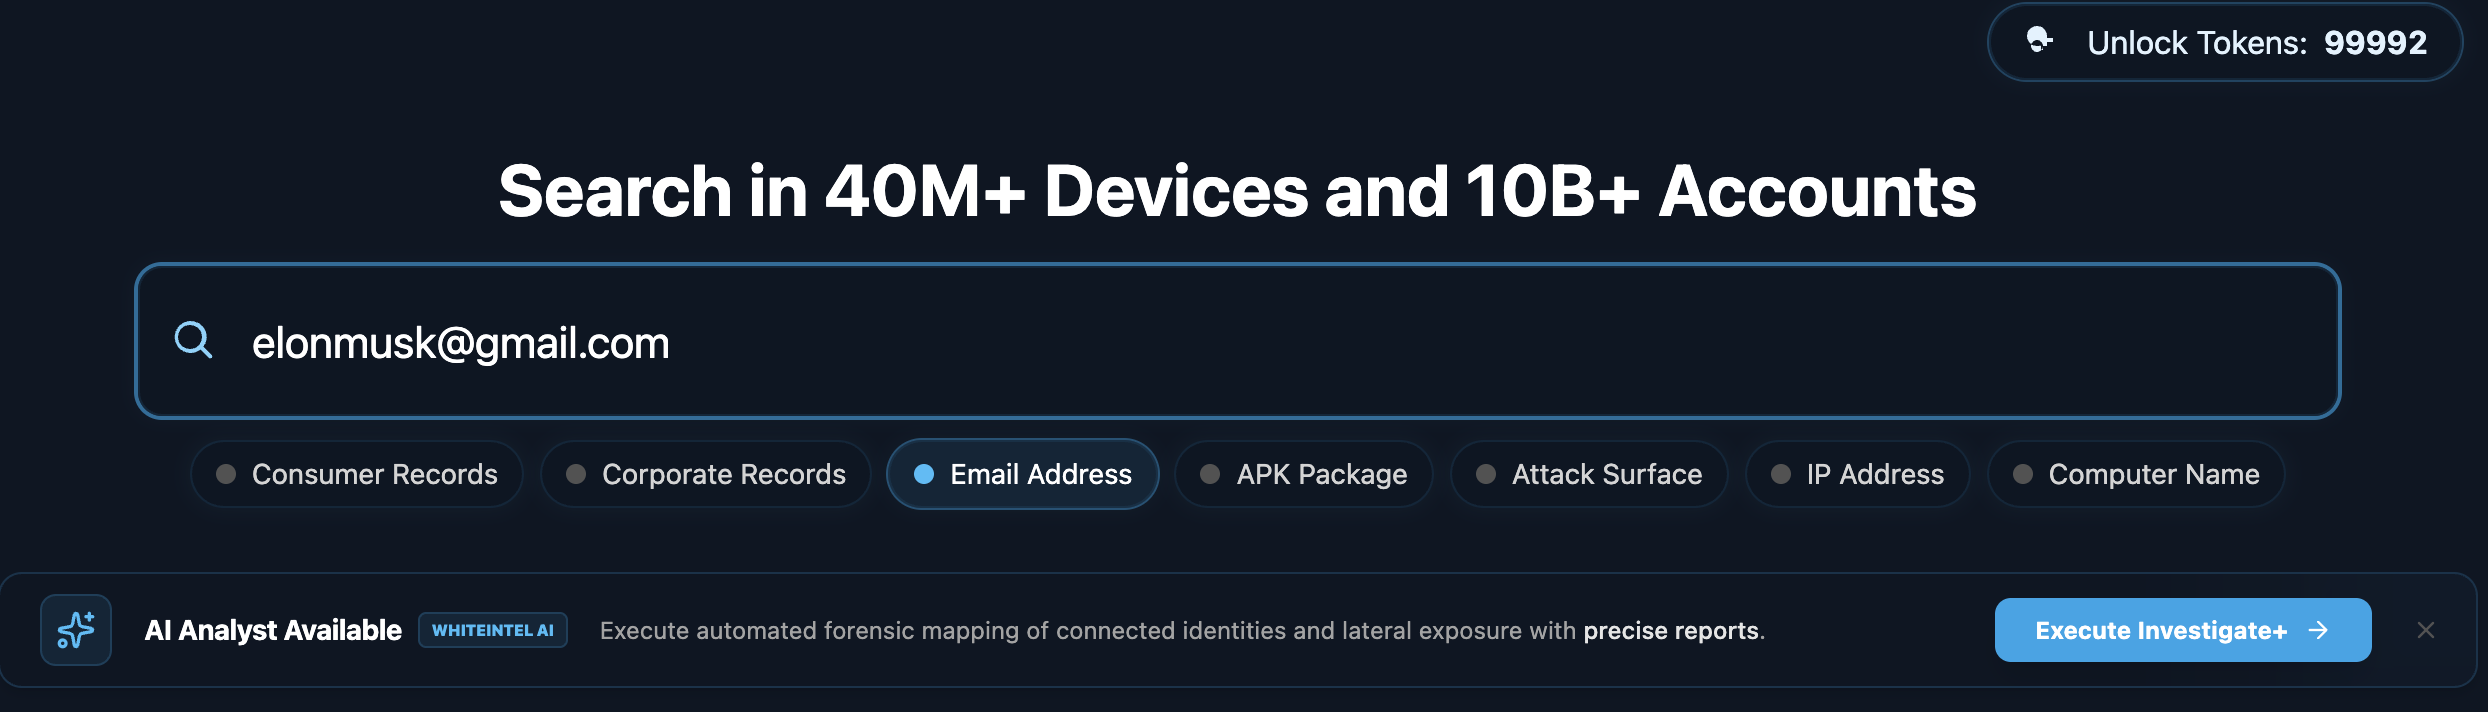
There are two primary ways to initiate a Neural Investigation. Currently, investigations are supported for usernames and email addresses.
#### Method A: The Investigations Tab
Users can navigate directly to the Investigations tab to manage existing cases or start a new manual lookup for a specific target identity.
#### Method B: Global Search Integration
When using the Global Search bar, the system will provide an indication if an AI Analysis is available for a given entry. This allows for a seamless transition from a general search to a deep forensic dive.
### 💳 Licensing & Access
Investigation+ is a premium feature requiring specific entitlements:
* Threat Intel License: Included by default for all users on the Threat Intel (tifirm) plan.
* Researcher/Enterprise Licenses: Available as an add-on for $1,500 USD / year.
To upgrade your access or purchase the add-on, please visit the Upgrades section in your dashboard settings.
[whiteintel.io](https://whiteintel.io)