# Platform overview

Whiteintel is a cybercrime intelligence platform that surfaces exposed credentials, infostealer infections, leaked records, look-alike domains, supplier risk, dark web mentions and payment-fraud indicators relevant to your organization. This page explains how the application is laid out and how to move between modules.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F4sLipyL5Vb3NSYPWjjHF%2Fresim.png?alt=media&amp;token=e17f37a3-83f0-41ce-9cd5-ad24bc0565c5" alt=""><figcaption></figcaption></figure>

### Navigation

All modules are reachable from the left navigation rail, which is present on every page. The rail can be collapsed to icons only to maximize working space, and the collapse state is remembered across sessions.

<div align="left"><figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FLOCsUP3L9EsKnOJgRees%2FNavigationbar.png?alt=media&amp;token=17e1c955-6b33-4103-a8af-b47793b290f4" alt="Whiteintel main navigation bar"><figcaption></figcaption></figure></div>

The rail groups features as follows:

* **Global Trends** and **Your Dashboard** — high-level analytics and your monitored assets.
* **Global Search** — direct lookups across the corpus.
* **Threat Feeds**, **Brand Protection**, **Supplier Security**, and **Payment Fraud** — intelligence modules.
* **Investigation+** — AI-assisted identity investigation.
* **Watchlist Events**, **Watchlists**, and **Saved Incidents** — monitoring and triage.
* **Profile**, **Organization**, **Webhooks**, **Upgrades**, **Contact**, and **API Docs** — account, administration, and integrations.

### Themes

The interface supports a light theme and a dark theme. Light is the default. The theme can be switched at any time from the control at the bottom of the navigation rail, and the preference is stored locally.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FPVYa42GmrdTUbdPg2JZL%2Fwhiteintel-white-and-dark-themes.png?alt=media&amp;token=c85284b5-5635-44f3-85ec-8ff26686d834" alt=""><figcaption></figcaption></figure>

### Where to go next

* To look up a specific identity, domain, or indicator, see Global Search.
* To monitor your own assets continuously, see Watchlists and Your Dashboard.
* To understand what your plan includes, see Subscriptions and licensing.


# Subscriptions and Licensing

Access to individual modules and to certain actions, such as CSV exports and multi-recipient alerts, is governed by your subscription tier and by whether your account belongs to an organization. This page summarizes how entitlements work.

### Account types

* **Individual account** — a single user with no organization. Some capabilities, including CSV exports and shared alert recipients, are unavailable to individual accounts.
* **Organization account** — multiple users under one organization, with shared entitlements, seats, and export credits. Organization administrators manage users, single sign-on, and the organization API key. See Organization settings.

### Subscription tiers

Higher tiers progressively unlock advanced modules and higher limits. The two tiers that unlock the most capability are **Enterprise** and **Threat Intelligence**.

Capabilities that are commonly tier-gated include:

* **CSV exports** of endpoints and raw records — available to organization accounts; raw record export additionally requires an Enterprise or Threat Intelligence subscription.
* **Watchlist groups** and **multiple alert recipients** — Enterprise or Threat Intelligence.
* **Brand Protection** (look-alike monitoring and takedowns) — Enterprise or Threat Intelligence.
* **Investigation+** — Threat Intelligence, or an add-on to Enterprise.
* **Webhooks** and several **identifier types** (IP, computer name) — Threat Intelligence.
* **Full log archive downloads** — Threat Intelligence.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FSdg2f8wSpi6N6tFL8evm%2Fresim.png?alt=media&amp;token=c9d457f7-6e1a-4f67-ba88-2abac834ec5e" alt=""><figcaption></figcaption></figure>

### How gating is presented

When a feature is not included in your plan, the platform still shows the feature so its value is visible, and marks it with a lock indicator and a short upgrade prompt. Opening a gated page presents an upgrade call to action rather than a generic error. Where an action would exceed a limit, the platform surfaces the specific reason, including required versus available credits.

### Export credits

CSV exports consume export credits, which are tracked at the organization level. See CSV exports and export credits for the cost model and how the balance is displayed and updated.

### Managing your plan

Plan changes and add-ons are handled from the **Upgrades** page, reachable from the navigation rail. For assistance, use the **Contact** page.


# Quickstart

This sections contains basic information about White Intel Dark Web & Data Breach search engine.

### What is Whiteintel

<figure><img src="https://imagedelivery.net/d5bS5FFwbZOwgmouc9uS9g/6d63f304-18a1-4ed7-76a9-cf29e3e92a00/w=800" alt=""><figcaption></figcaption></figure>

**WhiteIntel** is an advanced cyber threat intelligence platform designed to help organizations identify and respond to data exposures across the dark web, infostealer malware networks, and publicly accessible sources.\
Originally built as a specialized search engine for stealer-based credential leaks, Whiteintel has evolved into a comprehensive monitoring solution that offers multiple layers of protection.

WhiteIntel continuously monitors:

* **Infostealer malware logs** for exposed credentials, device data, and sensitive account information
* **Dark web ecosystems** (forums, TOR sites, marketplaces, paste sources) for brand or keyword mentions
* **Newly registered domain names** to detect look-alike domains targeting your organization
* **Public GitHub repositories for exposed secrets and code-based credential leaks**
* **Stolen credit cards and exposed bin** numbers

With unified search, automated alerting, and powerful API access, WhiteIntel enables organizations to quickly detect credential theft, brand impersonation attempts, and sensitive data exposures—providing actionable intelligence to reduce risk and strengthen overall security posture.

### Primary Use Case of Whiteintel

WhiteIntel enables organizations to identify and respond to **high-risk credential exposures** that threat actors commonly leverage in ransomware operations, fraud campaigns, supply-chain attacks, and account-takeover attempts.\
By providing real-time visibility into data leaked through information-stealer malware, dark web activity, and public code repositories, WhiteIntel helps security teams detect compromised accounts before they are weaponized.\
Because infostealer malware affects every sector—from finance and healthcare to technology and critical infrastructure—Whiteintel delivers essential intelligence for any organization that depends on digital systems and online services.

### Target Audience of Whiteintel

Although WhiteIntel provides value across a broad range of users, it is particularly impactful for:

* **Security Operations Centers (SOC)**
* **Threat intelligence teams**
* **Cybersecurity companies and MSSPs**
* **Incident response and DFIR practitioners**
* **Red teams, penetration testers, and offensive security professionals**
* **High-risk individuals or executives requiring enhanced digital protection**

Whether for defensive monitoring, proactive threat hunting, or offensive security research, WhiteIntel equips users with the intelligence needed to identify exposure, reduce attack surface, and strengthen overall security posture.

### **How to Try**

White Intel offers a free search feature that allows you to check if a domain has been compromised in information stealer-related breaches. Simply visit [whiteintel.io](https://whiteintel.io) to try it out instantly.


# Getting an Account

### Registration

You can sign up and create an account on the White Intel platform completely free using the [registration form](https://platform.whiteintel.io/signup).

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FoWTaerub2s29ctfwcgqj%2Fresim.png?alt=media&amp;token=612987a7-997e-4d04-8d0a-578d0fab6543" alt=""><figcaption></figcaption></figure>

### Account Activation

After creating an account, you will receive an email from the platform to verify and activate your account.


# Sign-in

To sign in to the White Intel platform, visit [platform.whiteintel.io](https://platform.whiteintel.io) or click the sign-in button on the main website of the [whiteintel](https://whiteintel.io).


# Interactive Demos

WhiteIntel's interactive demos are guided, click-through walkthroughs of the real product. Each one runs live in your browser — step through the workflow, hover the data, and see exactly how the platform works before you ever log in.

{% hint style="info" %}
**How to use these demos:** click the preview or **Start** on any demo below and follow the highlighted prompts. They're fully interactive — nothing is pre-recorded. Open any demo full-screen for the best view.
{% endhint %}

### Demo library

| Demo                        | What you'll see                                           | Category        |
| --------------------------- | --------------------------------------------------------- | --------------- |
| Your Dashboard Introduction | Get oriented in the dashboard, scoped to your domains     | Getting Started |
| Platform Overview           | Headline stats across the whole dataset                   | Getting Started |
| Global Trends               | Dark-web events, chatter, leaks, and threat news          | Getting Started |
| Global Leak Search          | Search leaks & stealer infections by any identifier       | Detection       |
| Payment Fraud Intelligence  | Validate compromised cards and watchlist BIN ranges       | Detection       |
| Supplier Security           | Continuously score third-party and vendor exposure        | Risk            |
| Brand Protection            | Track look-alike domains and impersonating infrastructure | Risk            |
| Threat Feeds                | Curated data sales, ransomware, and access listings       | Intelligence    |
| Investigation+              | Pivot across identifiers and unmask threat actors         | Intelligence    |

***

### Getting Started

#### Your Dashboard Introduction

Get oriented in the WhiteIntel dashboard — scope by watchlisted domain and see leaks, events, and records at a glance.

[![Your Dashboard Introduction — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_a83b7ea7-970b-48e2-b443-7646f76bbd18/page/1783695408316.png)](https://app.storylane.io/demo/s7jb0nhoba5x)

{% @storylane/embed subdomain="app" linkValue="s7jb0nhoba5x" url="<https://app.storylane.io/demo/s7jb0nhoba5x>" %}

#### Platform Overview

Your headline view of the platform — credentials, infected systems, adversaries, and ransomware across the entire dataset, updated daily.

[![Platform Overview — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_31d7855d-a8ff-4009-a9fc-9b67ea1816f1/page/kHDW3iF2Cli0ZMjCIalVr.png)](https://app.storylane.io/demo/yzypktmddjch)

{% @storylane/embed subdomain="app" linkValue="yzypktmddjch" url="<https://app.storylane.io/demo/yzypktmddjch>" %}

#### Global Trends

Track recorded dark-web events, chatter, credential leaks, infections, and threat news across the entire WhiteIntel dataset — your at-a-glance view of what's happening right now.

[![Global Trends — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_09e299f0-636a-4726-bb6b-3ca6d30c6f12/page/1781325398284.png)](https://app.storylane.io/demo/hth6g6nis2dg)

{% @storylane/embed subdomain="app" linkValue="hth6g6nis2dg" url="<https://app.storylane.io/demo/hth6g6nis2dg>" %}

***

### Detection

#### Global Leak Search

Search across credential leaks and stealer infections by domain, email, IP, password, and more. Validity is computed at query time, so you always act on what's true right now.

[![Global Leak Search — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_c9f1bb41-6243-4114-ae05-bd015a3ef610/page/1781419816586.png)](https://app.storylane.io/demo/jk5wrpz0kyzx)

{% @storylane/embed subdomain="app" linkValue="jk5wrpz0kyzx" url="<https://app.storylane.io/demo/jk5wrpz0kyzx>" %}

#### Payment Fraud Intelligence

Validate compromised cards and watchlist your BIN ranges. Investigate cards across the entire payment-fraud lifecycle, enriched with full issuer attribution.

[![Payment Fraud Intelligence — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_93b2417c-82ef-43f7-a705-305752f04e27/page/1781430769164.png)](https://app.storylane.io/demo/kqxrfvifzyxt)

{% @storylane/embed subdomain="app" linkValue="kqxrfvifzyxt" url="<https://app.storylane.io/demo/kqxrfvifzyxt>" %}

***

### Risk

#### Supplier Security

Score and monitor third-party and vendor exposure continuously. Detect compromised credentials across your supply chain and prioritize outreach by per-supplier risk.

[![Supplier Security — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_e1d26af4-d7e5-4073-8628-bc109405bcbd/page/1781427253372.png)](https://app.storylane.io/demo/cjq9uq3bhen5)

{% @storylane/embed subdomain="app" linkValue="cjq9uq3bhen5" url="<https://app.storylane.io/demo/cjq9uq3bhen5>" %}

#### Brand Protection

Track look-alike domains and brand-impersonating infrastructure. Surface phishing infrastructure and newly registered domains before they're weaponized against your customers.

[![Brand Protection — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_56579006-7e0a-480f-bbd7-47c47d368511/page/1781425792822.png)](https://app.storylane.io/demo/xyuqsqgvy0mh)

{% @storylane/embed subdomain="app" linkValue="xyuqsqgvy0mh" url="<https://app.storylane.io/demo/xyuqsqgvy0mh>" %}

***

### Intelligence

#### Threat Feeds

Curated dark-web telemetry: data sales, ransomware, and access listings — turned into early warning so you see threats taking shape long before they reach you.

[![Threat Feeds — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_566b6eed-c1c1-47be-b09d-114a9d593a62/page/1781422855990.png)](https://app.storylane.io/demo/1bh86msd4tnr)

{% @storylane/embed subdomain="app" linkValue="1bh86msd4tnr" url="<https://app.storylane.io/demo/1bh86msd4tnr>" %}

#### Investigation+

Pivot across identifiers and unmask threat actors with deep-trace analysis. Follow the connections between leaks, infrastructure, and adversaries in one workspace.

[![Investigation+ — preview](https://storylane-prod-uploads.s3.us-east-2.amazonaws.com/company/company_389e946a-14f8-4851-a6ae-3bd281d77288/project/project_64333627-a689-4b48-9f2a-6d9609999a98/page/1781434604688.png)](https://app.storylane.io/demo/hlltwqsryiuf)

{% @storylane/embed subdomain="app" linkValue="hlltwqsryiuf" url="<https://app.storylane.io/demo/hlltwqsryiuf>" %}

***

{% hint style="success" %}
**Want the full catalog?** Browse every demo in one place at the [WhiteIntel Demo Center](https://whiteintel.io/demo-center), or [book a live walkthrough](https://whiteintel.io/contact) with our team.
{% endhint %}


# Stealer Logs

Information stealers are a type of malware designed to collect and extract data from infected devices, including saved passwords from web browsers. Victims can become infected through various means, including downloading cracked software, accessing files from untrusted websites, or using activator applications. These methods often bypass security measures, making devices vulnerable to malware that can stealthily extract sensitive data. The information extracted from infected devices is often purchased, accessed, and utilized by threat actors to compromise systems, steal money, or demand ransoms.

A typical information stealer logs contains following information;

* Date of Infection
* Device system information which include Hostname, IP, Working Path, Antviruses
* Files from the destek of infected device
* Saved credentials from the infected devices' browsers

Followings are one the most common information stealer variants in wild;

* Raccoon
* Redline
* Luma
* Vidar&#x20;
* Stealc
* Monster

Despite the different variant names, they all offer similar data extraction services. The image below is an example of an information stealer log found on dark web resources.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FdjfqvzMlkFiPvOxyuBQc%2Fsample-log-1.jpg?alt=media&amp;token=f8b6de10-c9d3-4ff6-9496-831a4d1563ec" alt=""><figcaption><p>Sample Information Stealer Logs</p></figcaption></figure>

### Whiteintel Approach

White Intel continuously monitors dark web resources to detect, collect, and parse data, transforming it into actionable intelligence items.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FdsT0dYM7XdcnYcDscV9s%2Fresim.png?alt=media&amp;token=5bcaa691-8d8b-4858-bb6f-8f8ecbd585ad" alt=""><figcaption></figcaption></figure>


# Combolist Logs

Combo lists, a.k.a ULPs, are compilations of URL, username, and password information shared on dark web related resources. Due to the nature of these files, they do not include any additional information such as the date of the breach or details about the compromised device. They are simply lists of credentials in URL:USERNAME:PASSWORD format.

The following image contains part of a combo list detected on dark web related resources.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Fy76CfcunpMZmoGlM7Cav%2Fimage.png?alt=media&amp;token=fca66a1c-df85-4f0c-bae7-5e1841cf1ffb" alt=""><figcaption></figcaption></figure>

### Difference Between Information Stealer Logs and Combo lists

Information stealer logs include additional data such as IP addresses, host-names, usernames, operating systems, malware paths, files, the date of compromise, and saved credentials from the browsers. In contrast, combo lists are merely lists of credentials without any supplementary information, making them less reliable compared to comprehensive information stealer logs.

### Whiteintel Approach

Whiteintel offers a filter differentiate between information stealer logs and combo lists.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FWmXG7P5mgMQTlbS1fTV6%2Fresim.png?alt=media&amp;token=92dd6909-4e70-4164-9454-f3ac2bcaafba" alt=""><figcaption></figcaption></figure>


# Consumer Records

Consumer Records represent credential exposures that **do not belong to the organization’s corporate domain**.\
For example, when monitoring **acme.com**, any leaked account that is **not** in the format **`<user>@acme.com`** is classified as a Consumer Record.

This includes:

* Personal email addresses (e.g., Gmail, Yahoo, Outlook) used by employees or third-party users
* Accounts identified **only by usernames** with no associated corporate email
* Credentials originating from infostealer infections or breached platforms where users signed up using non-corporate identities

By separating Consumer Records from corporate-domain leaks, Whiteintel enables organizations to clearly identify **direct corporate exposures** while still assessing potential risks such as password reuse, supply-chain access, and lateral movement.


# Corporate Records

Corporate Records represent credential exposures that are **directly associated with the organization’s official domain**.\
When monitoring **acme.com**, any leaked account in the format **`<user>@acme.com`** is classified as a Corporate Record.

Corporate Records typically include:

* Employee accounts registered with the organization’s corporate email domain
* Credentials exposed through infostealer malware, third-party breaches, or compromised SaaS platforms
* Accounts tied to internal or business-critical services (e.g., VPN, email, cloud platforms, developer tools)

Because these records originate from verified corporate identities, they indicate **direct organizational exposure** and often require immediate attention.\
Corporate Records help organizations:

* Identify high-risk account compromises
* Prioritize remediation actions for business-critical accounts
* Reduce the risk of unauthorized access, internal system breaches, and account takeover attacks

By distinguishing Corporate Records from Consumer Records, Whiteintel ensures clear visibility into **high-impact incidents involving official corporate credentials**.


# Look-Alike Domains

Look-Alike Domains refer to newly registered domain names that **visually or textually resemble an organization’s official domain**.\
WhiteIntel continuously monitors **daily domain registrations worldwide** to identify domains that mimic your brand or corporate identity.

When monitoring **acme.com**, examples of look-alike domains include:

* `acme-secure.com`
* `acme-login.net`
* `acrne.com` (character substitution)
* `acme-support.org`
* `acme.co` (TLD variations)

These domains are often created for:

* Phishing attacks
* Credential harvesting
* Malware distribution
* Impersonation attempts
* Fraudulent customer communication
* Supply-chain deception

Whiteintel automatically analyzes each newly registered domain using similarity algorithms to determine whether it resembles your protected domain.\
When a match is detected, the domain is added to your **Look-Alike Domain Records**, along with supporting metadata such as:

* Registration date
* Registrar and WHOIS details (when available)

Monitoring look-alike domains enables organizations to:

* Detect early signs of brand impersonation
* Identify potential phishing infrastructure
* Initiate takedown actions before malicious activity escalates
* Strengthen overall brand protection and external attack surface defense

By proactively tracking daily domain registrations, Whiteintel gives organizations clear visibility into evolving threats targeting their brand identity.


# Dark Web Mentions

Dark Web Mentions refer to detections where one of your configured keywords appears on **dark web sources** monitored by WhiteIntel.\
Organizations can define keywords such as brand names, product names, executive names, or any other terms relevant to their risk profile.

Whiteintel continuously monitors a wide range of dark web resources, including:

* Hacker forums
* TOR-based marketplaces
* Cracking communities
* Leaked database hubs
* Underground chat platforms
* Paste sites and anonymous sharing services

When a monitored keyword appears on any of these sources, Whiteintel generates a **Dark Web Mention Record**, providing:

* The detected keyword
* Timestamp of the discovery
* Source type (forum, marketplace, chat, TOR site)
* Contextual text surrounding the mention (when available)
* Link or reference to the original post or resource

Examples of useful keywords include:

* Organization name: `Acme`
* High-value products: `Acme Cloud`
* Executive or VIP names: `John Doe`
* Internal project names or codewords
* Supply-chain partner names

Dark Web Mention monitoring allows organizations to:

* Detect discussions related to targeted attacks
* Identify leaked internal data or credentials being shared
* Spot brand impersonation or fraud attempts
* Track threat actor activity involving the organization
* Respond early to emerging risks before they escalate

By enabling keyword-based monitoring across dark web ecosystems, Whiteintel provides actionable visibility into threats that may otherwise remain hidden.


# Exposed Source Code

Whiteintel monitors public GitHub repositories to detect **exposed secrets**, such as credentials, API keys, tokens, and other sensitive information that may have been accidentally committed to source code.\
This capability helps organizations quickly identify and mitigate risks arising from leaked secrets within their own repositories or third-party code linked to their ecosystem.

When monitoring repositories, Whiteintel detects exposures such as:

* API keys (AWS, GCP, Azure, Stripe, etc.)
* Database connection strings
* Access tokens and OAuth credentials
* SSH keys and private keys
* Hard-coded passwords
* Cloud provider credentials
* Configuration files containing sensitive data
* Secrets embedded in commit history

For each detected secret, Whiteintel provides:

* Repository name and path of the exposed file
* Commit ID where the secret appears
* Line numbers and surrounding context
* Type of secret and risk classification
* Timestamp of detection
* Unique hash for deduplication
* Downloadable CSV evidence for auditing and response

Organizations use GitHub secret exposure monitoring to:

* Prevent unauthorized access to cloud environments and internal systems
* Detect accidental credential leakage during development
* Audit third-party repositories for supply-chain risks
* Track and respond to sensitive information leaked through commit history
* Strengthen DevSecOps and secure SDLC practices

By continuously scanning public GitHub repositories, Whiteintel provides proactive detection of secret exposures—reducing the risk of account compromise, data breaches, and infrastructure misuse stemming from leaked developer credentials.


# Global Search

Global Search queries the Whiteintel corpus directly for a specific identity, asset, or indicator and returns matching records. It is the fastest way to investigate a single value without configuring continuous monitoring.

**Availability:** All plans. Certain search types and result detail are tier-gated, as noted below.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FVXnpou9JMIDbGbANlbLU%2Fresim.png?alt=media&amp;token=cda65932-ed1d-4504-b83d-a888f961025a" alt=""><figcaption></figcaption></figure>

### Running a search

1. Select a **search type** that matches the value you are looking up.
2. Enter the value in the search bar and run the search.
3. Review the results in the table on desktop, or as stacked cards on mobile.

The search type and query are reflected in the page URL, so a search can be bookmarked, shared, or reopened in a new tab with the same parameters.

### Search types

* **Consumer records** — leaked accounts associated with a domain where the account holder is an external consumer (for example, a personal email used on the site).
* **Corporate records** — leaked accounts where the username belongs to the searched domain itself.
* **Email address** — records tied to a specific mailbox.
* **IP address** — records observed in connection with an address. Requires a Threat Intelligence tier.
* **Computer name** — records tied to a device hostname. Requires a Threat Intelligence tier.
* **Country** — records filtered by country. Country values use the ISO two-letter code.
* **Password** — lookups by password. Password queries require a minimum length.
* **APK package** — records tied to a mobile application package.
* **Attack surface** — exposed assets and services associated with a domain.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FGYxTfgJBWdAdaOJW3A9K%2Fresim.png?alt=media&amp;token=32a60d50-7eac-4652-879a-f7275b1a25a0" alt=""><figcaption></figcaption></figure>

### Filters

The Filters panel refines the active result set without starting a new query. Common filters include:

* **Subdomain** and **Domain** scoping.
* **Date range** or a specific event date.
* **Log type**, where applicable: stealer, combolist, or database.

On all viewport sizes the Filters panel opens as an overlay so it does not reflow the results behind it.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Fg9i1SiblpgjdzrxV5u7l%2Fresim.png?alt=media&amp;token=31b996ed-f526-4347-80a5-63654c954597" alt=""><figcaption></figcaption></figure>

### Results

Each result row summarizes the leaked account, the application or URL it was captured on, the record class, the source type, and when it was last seen. Selecting a row opens the detail view; see Viewing logs and record detail.

On mobile, results render as cards that present the same fields in a stacked layout.

### Saved and recent searches

Frequently used queries can be saved for reuse, and recent searches are retained so you can return to them quickly.


# Viewing logs and record detail

Selecting a record from Global Search, the Dashboard, or a monitoring view opens the detail sidebar. The detail sidebar is the primary surface for examining a single compromised identity and the device it was captured from.

**Availability:** All plans. Full log archive downloads require a Threat Intelligence subscription.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FqUhBz6rzNpsxu0l6kYR6%2Fresim.png?alt=media&amp;token=9465dcd6-23b7-40b4-bd23-243f867bdd98" alt=""><figcaption></figcaption></figure>

### Layout

The detail sidebar opens from the right and is organized into tabs:

* **Summary** — a narrative description, device metadata, and the exposed credentials.
* **History** — every recorded sighting of the device, presented as an audit trail.
* **Downloads** — full log archives, when available for the record.

The Downloads tab appears only when at least one downloadable archive exists for the record.

### Summary tab

#### Description

A short narrative explains how the identity and credentials were compromised and the recommended remediation, such as rotating passwords, revoking sessions, and enforcing multi-factor authentication.

#### Meta data

The metadata grid shows device attributes such as hostname, IP address, country, operating system, anti-virus, and the relevant dates. The most recent sighting is shown first.

When the most recent record does not contain a particular attribute, the platform fills the gap with the most recent earlier sighting that does, and marks that value with a small clock indicator. A footer note explains the convention, and hovering the value reveals the date it was observed. Attributes that changed across sightings always show the latest known value rather than an older one.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Flty1QmzsxHbaPcQky1Re%2Fresim.png?alt=media&amp;token=0806905d-fa8d-4420-b73a-3d758fbe641c" alt=""><figcaption></figcaption></figure>

#### Exposed credentials

Credentials are listed with the application or URL, the username, the password, and the capture date. Passwords are masked by default. They can be revealed individually, or all at once using the reveal control at the top of the section. Where supported, captured cookies and session data are also available.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FlbkM5KXWv1WNg2cCl9Dz%2Fresim.png?alt=media&amp;token=a7f1258e-c962-436e-ad55-6aed360ae4f5" alt=""><figcaption></figcaption></figure>

### History tab

The History tab lists every sighting of the device, newest first, so an analyst can trace how the device's attributes and exposure changed over time. Internal bookkeeping fields are omitted so the view stays focused on meaningful attributes.

### Downloads tab

When a full log archive has been retained, it can be downloaded from this tab. Archive availability is indicated per record, and downloads require a Threat Intelligence subscription. Archives that are still uploading or that failed are labeled accordingly.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FkGfnj9BS9EJMs8gBIfqh%2Fresim.png?alt=media&amp;token=cf709ec6-2263-45a5-ab49-4860fd478c9d" alt=""><figcaption></figcaption></figure>

### Access restrictions

Record detail is subject to rate limits and entitlement checks. If access is temporarily restricted, the sidebar shows a clear notice rather than failing silently. Session expiry returns you to sign-in.


# Global Trends

Global Trends presents aggregate, time-based analytics across the WhiteIntel corpus. Where Global Search answers questions about a single value, Global Trends provides macro context: how exposure volumes are moving over time and where activity is concentrated.

**Availability:** Refer to your plan for the level of analytics included.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F2ANWEKQd8s5xFVXXu90r%2Fresim.png?alt=media&amp;token=7f811f17-1d80-4ce8-88e1-dec3e0f6b4e0" alt=""><figcaption></figcaption></figure>

### What it shows

Global Trends is intended as an at-a-glance briefing surface. Typical content includes:

* Headline metrics that summarize current exposure volumes.
* Time-series charts showing how those volumes change across a selected window.
* Breakdowns that highlight where activity is concentrated.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F52RonESBJ8rOhAADGQTJ%2Fresim.png?alt=media&amp;token=c592cdec-c5d3-4110-99ac-f083758a11c6" alt=""><figcaption></figcaption></figure>

### Reading the charts

Charts are temporal by design: the horizontal axis represents time and the vertical axis represents counts. Use the range and bucket controls, where present, to widen or narrow the window and to change the granularity from daily to weekly or monthly.

Empty leading and trailing periods are trimmed so the visible range reflects the data rather than the full requested window.

### Using Global Trends in an investigation

Global Trends is most useful as a starting point. When a chart indicates a spike or a concentration of activity, move to Global Search to examine the underlying records, or to Your Dashboard to see how the trend affects your monitored assets specifically.


# Investigation+

Investigation+ is an AI-assisted identity investigation tool. Given an email address or username, it correlates the identity across infostealer records and assembles a consolidated profile of the devices, accounts, applications, and credentials associated with it.

**Availability:** Threat Intelligence subscription, or an add-on to Enterprise. Usage is rate limited.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FdFUWjBd0fU7z9e6VAKJe%2Fresim.png?alt=media&amp;token=930348fa-5263-4fad-830d-74b941f97551" alt=""><figcaption></figcaption></figure>

### Starting an investigation

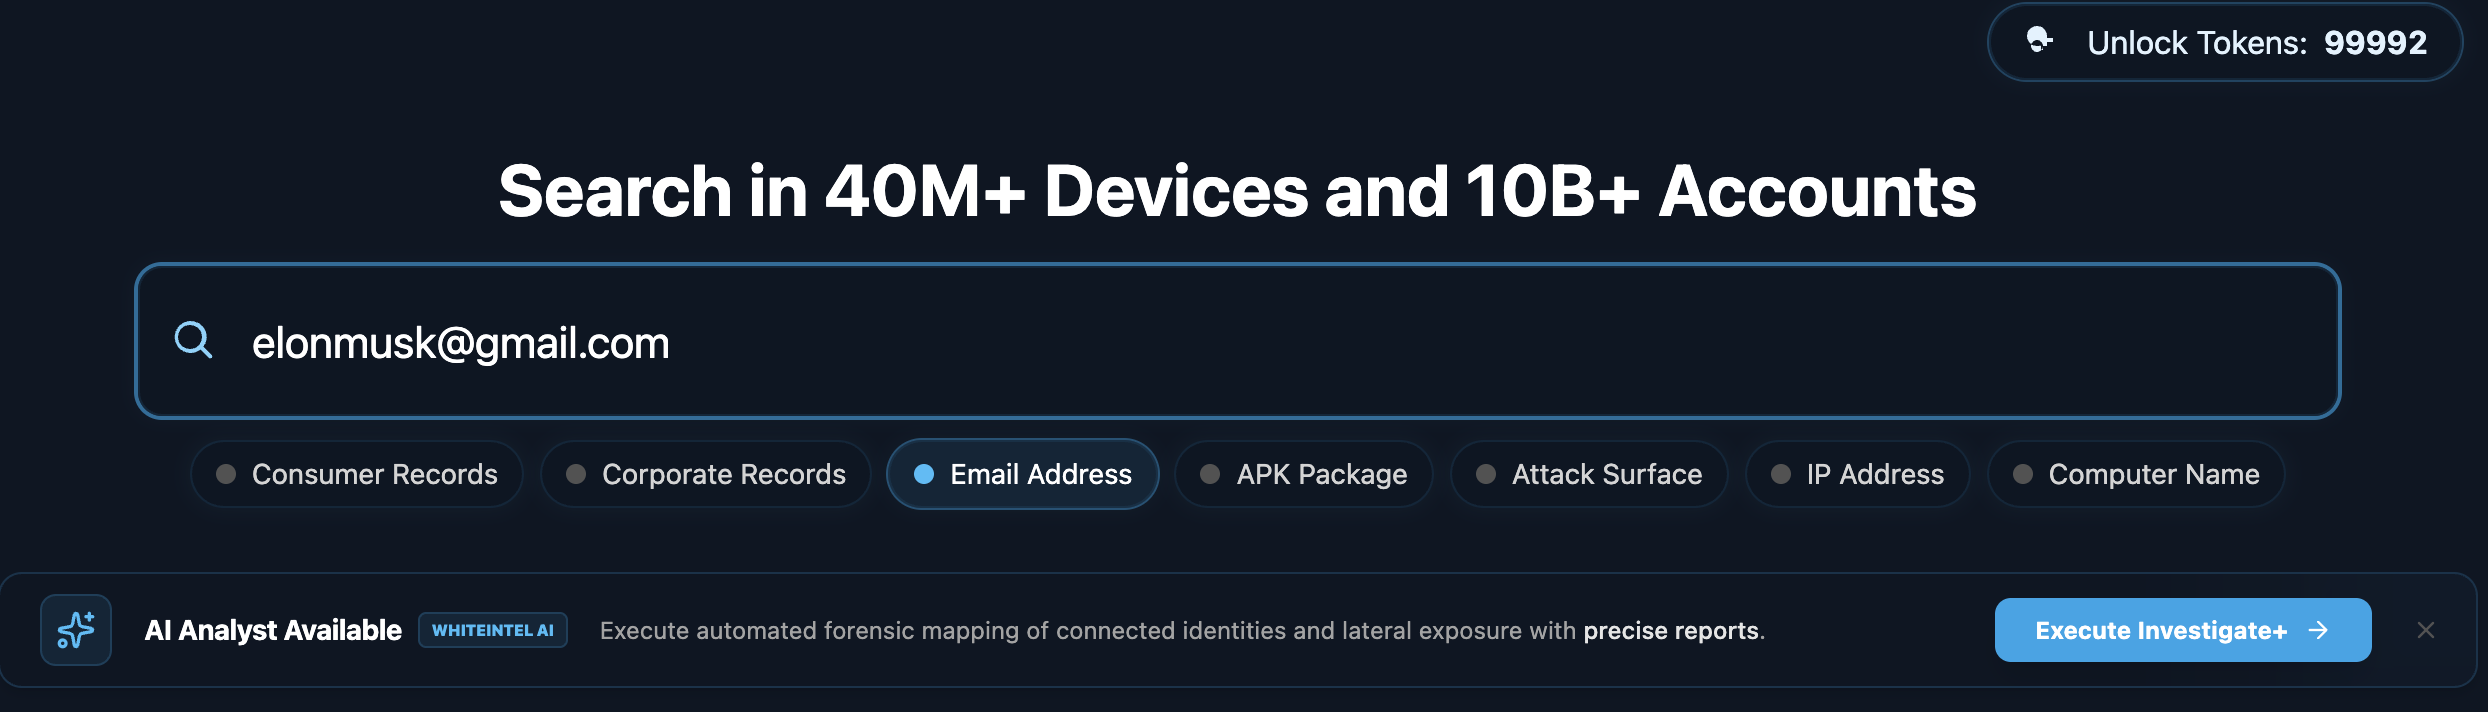
1. Enter an email address or username in the search field and run the analysis.
2. The platform queues an analysis job and processes it in stages. Progress is shown per component while the job runs.
3. When the job completes, the consolidated results are displayed.

Each analysis is recorded in your **Analysis History**, so a previous investigation can be reopened without re-running it.

### Usage limits and accuracy

Investigation+ is AI-assisted and may contain inaccuracies. Usage is capped per hour and per day. The applicable limits are shown on the landing view, and the platform reports a clear message if a limit is reached.

### Results

When an identity is found, the results are organized into tabs:

* **Results** — a Known Assets panel and an Applications footprint.
  * **Known Assets** groups the device-level attributes correlated with the identity: computer names, operating systems, IP addresses, countries, related accounts discovered on the same compromised devices, and recovered passwords.
  * **Applications footprint** lists the applications and services associated with the identity.
* **Graph** — a visual relationship map between the identity and the correlated entities.
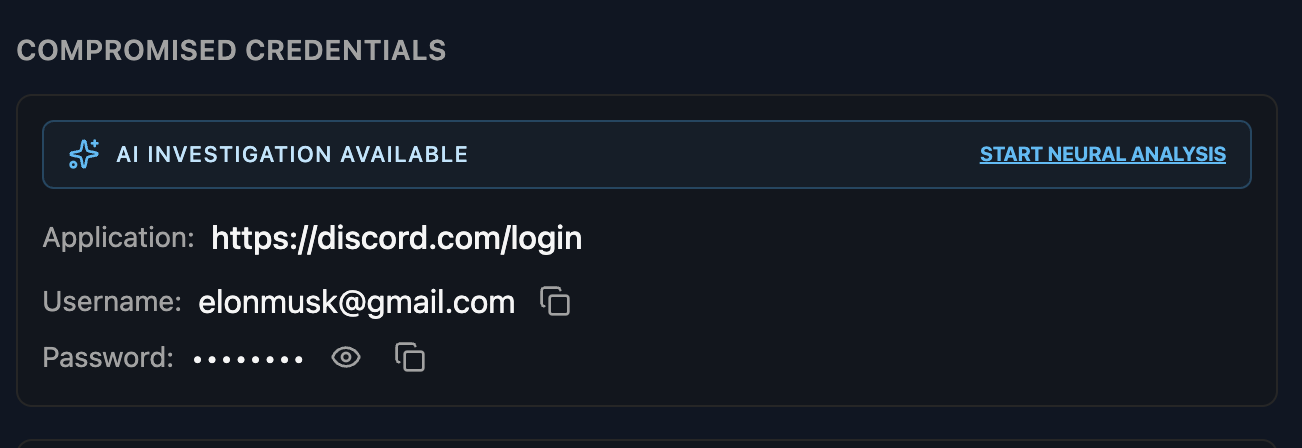
* **Credentials** — the exposed credential records tied to the identity.
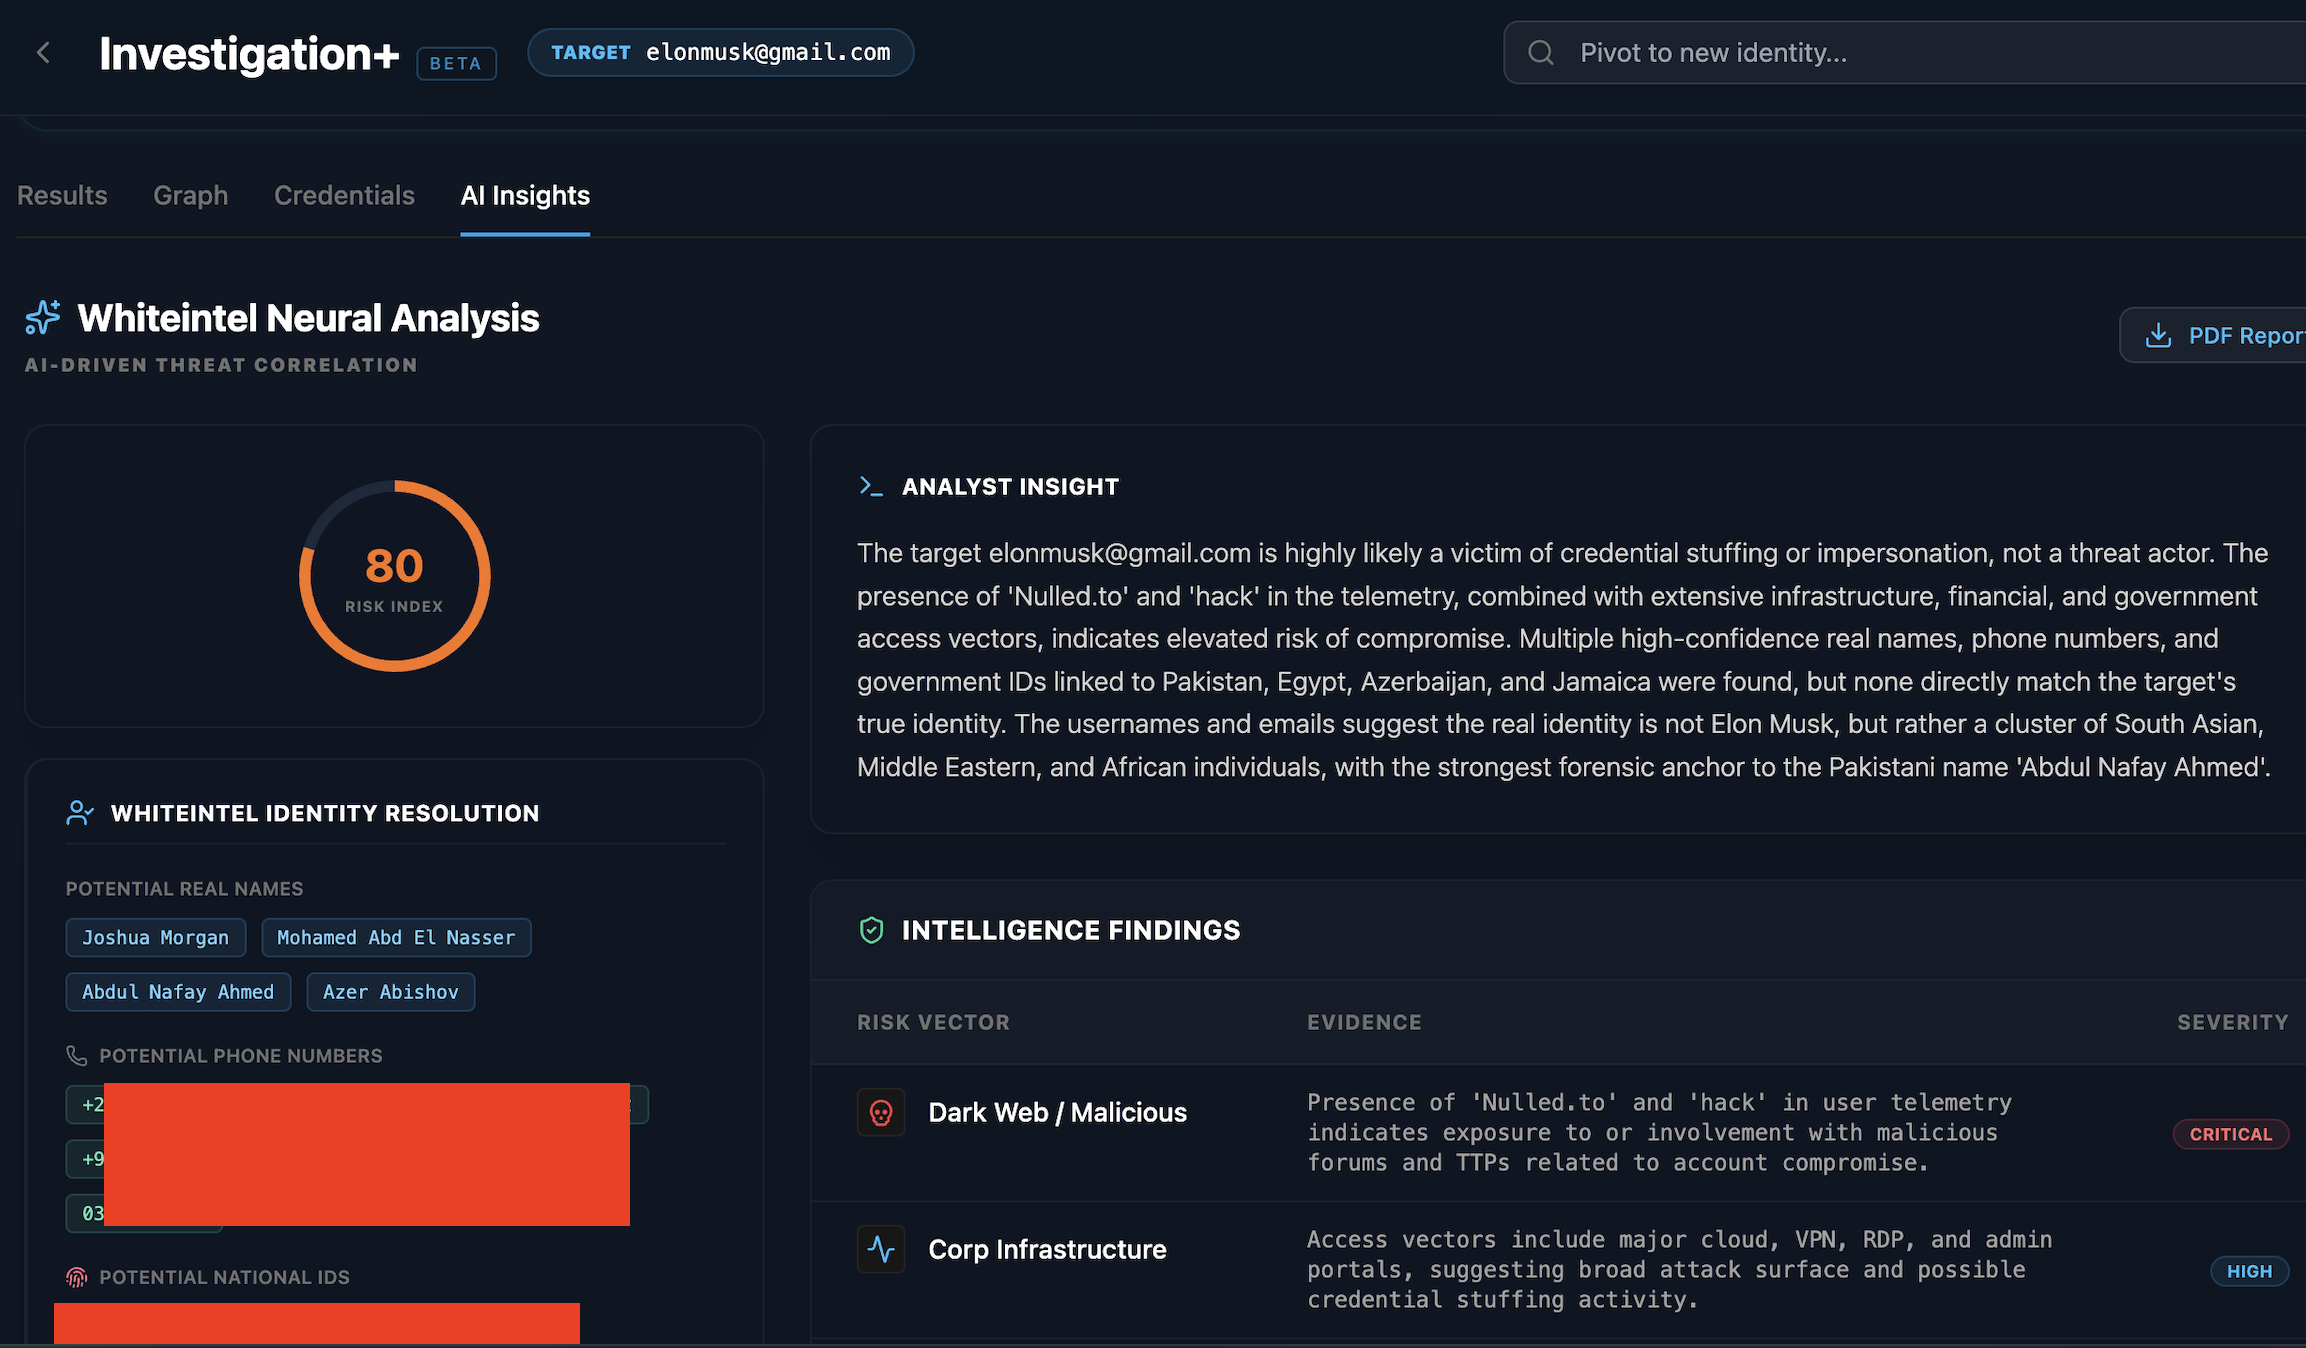
* **AI Insights** — a generated narrative analysis of the findings.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FDNPlWSCfvGA1A8pL9Wul%2Fresim.png?alt=media&amp;token=8f94724b-b0e4-40fd-b4cf-22be27d540ec" alt=""><figcaption></figcaption></figure>

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FMRynY6VMTVtedEHoNlnO%2Fresim.png?alt=media&amp;token=b588f660-2f39-46fe-84da-ed65b13b3f03" alt=""><figcaption></figcaption></figure>

### Exporting findings

The assembled asset data can be exported as a structured file for offline analysis or inclusion in a report.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F5QT5W62VMUMxD7dgfgiC%2Fresim.png?alt=media&amp;token=d97c35f6-1c8d-4316-86c7-b23d498961c4" alt=""><figcaption></figcaption></figure>

### No results

If the analysis completes but no matching infostealer records are found, the platform states this explicitly and offers to return to the search so you can investigate a different identity.


# Dashboard overview

Your Dashboard is the domain-scoped workspace. It opens on a landing view that lists the domains and watchlist groups you monitor, and lets you drill into any one of them for a detailed exposure picture.

**Availability:** All plans. Group views and some tabs are tier-gated, as noted on their pages.

### Watchlisted domains table

The landing view lists every monitored domain with, for each:

* the domain,
* the most recent event,
* the newest corporate record and newest consumer record,
* the date it was added to your watchlist,
* and the total number of leaks.

The **Last event** column header is a sort control: clicking it cycles through latest-first, oldest-first, and unsorted, so you can surface the assets with the most recent activity.

Domains that belong to a watchlist group are collapsed into a single expandable group row, which can be expanded to show its members or opened to scope the whole dashboard to that group.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FuLWXDxR0buagIvz2wjTq%2Fresim.png?alt=media&amp;token=be1319b1-15c1-41fd-b78c-5800d8be4f68" alt=""><figcaption></figcaption></figure>

### Domain detail view

Selecting a domain or group scopes the dashboard to it and presents a tabbed detail view:

* **Overview** — headline metrics, exposure trends, recent exposure breakdown, and dark web visibility.
* **Credentials** — the leaked records for the domain. See Credentials.
* **Endpoints** — infected corporate machines carrying records for the domain. See Endpoints.
* **Applications** — third-party applications associated with the domain's exposed accounts. See Applications.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Fye1eleMtl2IgwKuKD4y4%2Fresim.png?alt=media&amp;token=00d046e1-f489-4746-b808-3d619cb616f7" alt=""><figcaption></figcaption></figure>

### Group scope

When viewing a watchlist group, a Group Domains control in the header lets you narrow the entire view to a single member domain, or view all members aggregated. This control scopes the Overview, Credentials, Endpoints, and Applications tabs consistently.

### Overview tab

The Overview tab presents top-line counts, time-series charts for consumer and corporate exposure, a recent-exposure breakdown across sources, and dark web mention visibility. Counts that reach a backend cap are shown with a plus suffix.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FTu10MtaBCu1rCKuFdMia%2Fresim.png?alt=media&amp;token=a144a1fa-1f74-4b37-b832-f29d56eb30cc" alt=""><figcaption></figcaption></figure>


# Credentials

The Credentials tab of the Dashboard lists the leaked credential records for the selected domain or watchlist group. It merges consumer and corporate records into one feed and lets you filter, sort, and drill into any record.

**Availability:** All plans. CSV export of raw records requires an organization account on an Enterprise or Threat Intelligence subscription.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FLJ9XNILnwaT80YaJ2GxU%2Fresim.png?alt=media&amp;token=af1f2b87-3304-48e0-bab6-3fa079a7e611" alt=""><figcaption></figcaption></figure>

### Reading the table

Each row represents one leaked record and shows the leaked account, the application or URL it was captured on, the record class, the source type, and when it was last seen. In group views, a source column indicates which member domain the record belongs to. The header reflects the active record class, for example "Consumer Credential Records for example.com".

### Filtering and sorting

The filter bar provides:

* **Records** — All, Consumer, or Corporate. This is a client-side filter applied to the loaded feed.
* **Log type** — All, Stealer, Combolist, or Database, sent to the backend.
* **Show latest added** — one-click predefined views that narrow to a record class and sort by date added.
* **Sort by** — Log date or Latest added.

A Reset control clears the active filters.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FTQuBTwvfcntgx3fRzpWp%2Fresim.png?alt=media&amp;token=8b7cdd51-3166-47ef-b877-fb0f00b93c73" alt=""><figcaption></figcaption></figure>

### Record detail

Selecting a record opens the shared detail sidebar, which presents the device metadata and the exposed credentials. See Viewing logs and record detail.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FEuy5hUwqDrqyf9r9NTEe%2Fresim.png?alt=media&amp;token=30b7b359-b27d-48e5-be66-5f9020e7d5be" alt=""><figcaption></figcaption></figure>

### Exporting

The **Export** button opens a slide-over that exports the full record set server-side as a CSV file. The export is billed against your organization's export credits and requires an Enterprise or Threat Intelligence subscription. You choose the record type, a date range, and optional infected-system columns. See CSV exports and export credits.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FtIeF4tuFaJnajv4eBDZ4%2Fresim.png?alt=media&amp;token=ca238fa9-0bb3-4c6d-a866-b03a4ddd08b1" alt=""><figcaption></figcaption></figure>


# Endpoints

The Endpoints tab of the Dashboard lists infected corporate machines that carry at least one corporate credential record for the selected domain or watchlist group. It is the device-centric counterpart to the Credentials view.

**Availability:** All plans for viewing. CSV export requires an organization account and, per platform policy, an Enterprise or Threat Intelligence subscription.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F7mPnJy0uv1rANTIMHuPl%2Fresim.png?alt=media&amp;token=17d48601-7a08-43e7-b8d8-1ff737b4a123" alt=""><figcaption></figcaption></figure>

### Reading the table

Each row represents one infected machine and shows:

* the source domain (in group views),
* the hostname,
* the IP address,
* the operating system, with a brand icon,
* the country, with a flag,
* the count of corporate credential records on the machine,
* and the date it was last seen.

A trailing action opens the endpoint detail. On mobile, machines render as cards that present the same fields stacked.

### Sorting

A Sort by control orders the list by last seen or by latest added. In group views, restricted domains are skipped and reported as a count.

### Endpoint detail

Selecting an endpoint opens a detail sidebar scoped to that machine, presenting:

* a description of the infection,
* a metadata grid for the device, and
* the exposed corporate credentials, with passwords masked by default and revealable, plus remediation guidance.

The detail sidebar also offers a client-side export of the metadata and the credentials currently loaded on the sidebar, for quick capture of a single machine.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FUBgyhqv0O5T6E7fCT2nJ%2Fresim.png?alt=media&amp;token=8bb73a28-480a-46d3-9e98-5da63641253e" alt=""><figcaption></figcaption></figure>

### Exporting

The **Export** button opens a slide-over that exports the full endpoint set server-side as a CSV file, billed against your organization's export credits. In group views you can scope the export to all domains or to a single member. See CSV exports and export credits.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FY7guAoy0mevSQjGRnY7M%2Fresim.png?alt=media&amp;token=6dbee518-46e2-4419-ae14-380edba42645" alt=""><figcaption></figcaption></figure>


# Applications

The Applications tab of the Dashboard lists the third-party applications that a domain's exposed accounts also appear on. It helps you understand the wider footprint of a compromise: the external services where the same identities are exposed.

**Availability:** All plans for viewing.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FHgAjhTHbD2rKkG9rTgl5%2Fresim.png?alt=media&amp;token=f38a3570-3e2d-4760-9749-091d3cb0f163" alt=""><figcaption></figcaption></figure>

### What it shows

Applications are split into two classes:

* **Consumer** — Regular users (personal email addresses, direct usernames) that has access to the specified application.
* **Corporate** — Users with **corporate email prefix** that has access to the specified application.

In group views, a source column attributes each application to the member domain it relates to. Each application is itself a registrable domain.

On mobile, applications render as cards that present the application, its type, and the source, with a View records action.

### Filtering and search

* **Show** — All, Consumer, or Corporate.
* **Search** — a substring match on application names.

Both are applied server-side, so the totals and pagination reflect the filtered result.

### Viewing records

Each application row provides a **View records** action that opens Global Search in a new tab, pre-scoped to the source domain and filtered to the selected application, with the matching record type. This lets you move directly from "where else is this domain exposed" to the underlying records.

### Population time

Initial application results may take up to twelve hours to populate for a newly monitored domain. The view states this explicitly when no results are available yet, which is distinct from the case where an active filter simply matches nothing.


# Watchlists

Watchlists define the assets WhiteIntel monitors on your behalf. Adding an identifier to a watchlist enables continuous detection and alerting for that asset, and populates the corresponding views in Your Dashboard and Watchlist Events.

**Availability:** All plans. Groups and multiple alert recipients require an Enterprise or Threat Intelligence subscription. Some identifier types require a Threat Intelligence subscription.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FisN6uf0LOLr6E21rVRMf%2Fresim.png?alt=media&amp;token=44663579-e66b-4380-bba5-6f5c0b8e846d" alt=""><figcaption></figcaption></figure>

### Identifier types

* **Domain** — a registrable domain. Triggers on leaks against the website or any account using that email domain.
* **Subdomain** — a specific host to monitor independently. Subdomains share the domain quota.
* **Email address** — an individual mailbox.
* **IP address** and **Computer name** — device-level identifiers. Require a Threat Intelligence subscription.
* **Keyword** — a free-text term to monitor for dark web mentions.
* **Github repository** — a repository to monitor for exposed secrets.

A Definitions tab on the page describes each type and the tier required to use it.

<div align="left"><figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Fo1S4vqe9rPuLySlhCKIo%2Fresim.png?alt=media&amp;token=4e13ded6-85d7-4fa1-a4ea-0b176dd3402f" alt=""><figcaption></figcaption></figure></div>

### Adding an identifier

1. Choose the identifier type and enter the value.
2. For domains and subdomains, choose the **Record type** to alert on: corporate, consumer, or both.
3. Choose who to notify, and any delivery options.
4. Review the summary and confirm.

Each identifier type draws from its own pool of available identifiers in your subscription. The form shows how many remain and links to upgrade when a pool is exhausted.

### Notifications and recipients

The primary recipient is the signed-in user's email by default. On Enterprise and Threat Intelligence subscriptions, one additional recipient can be added from your organization's members. Individual accounts can only notify their own email.

### Delivery options

Depending on the identifier type and your integrations, you can enable:

* **Detect look-alike domains** (for domains),
* **Push to Jira**,
* **Push to Slack**,
* **Include usernames as CSV** in alerts.

Options that require an integration or a higher tier are shown with the relevant indicator.

### Groups

On Enterprise and Threat Intelligence subscriptions, identifiers can be filed under groups, such as one group per business unit or subsidiary. Groups can be created, renamed, color-coded, and deleted, and identifiers can be assigned individually or in bulk. Group views are then available throughout the Dashboard.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FoO5U9KLqre04w6dlVxRf%2Fresim.png?alt=media&amp;token=e5e88fcd-4f1f-45a0-9709-a526aff079fb" alt=""><figcaption></figcaption></figure>


# Watchlist Events

Watchlist Events is the continuous alert feed for the assets you monitor. Every detection against a watchlist identifier appears here as an event, ready for review and triage.

**Availability:** All plans, for the identifiers your subscription permits.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FDaJZLv2H90XBJ20wAgdJ%2Fresim.png?alt=media&amp;token=47e8480c-9c45-4b55-b231-73e38ec1ce70" alt=""><figcaption></figcaption></figure>

### Event-type tabs

A tab strip below the page header filters the feed by event type:

* **All** — every event.
* **Leaks** — credential leaks from stealer and combolist sources.
* **Mentions** — dark web mentions.
* **Exposed Secrets** — exposed repository secrets.

The selected tab and sub-tab are reflected in the page URL, so a view can be bookmarked or refreshed in place.

<div align="left"><figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F5VgClhde1hMWXPdFXk1o%2Fresim.png?alt=media&amp;token=7e9b5231-3537-4227-af00-c8a16603775a" alt=""><figcaption></figcaption></figure></div>

### Filters

The toolbar refines the feed by:

* **Identifier** — a specific monitored domain, keyword, or watchlist group.
* **Date range** — a quick range such as the last 7, 30, or 90 days.
* **Status** — open, resolved, or unresolved.

A time-series card alongside the list summarizes event volume over the selected range, with a day, week, or month bucket selector.

### Reading an event

Each event is presented as a card with a generated title that states the audience, the action, and the subject, along with the credential count, the entry, tags for type and status, and the affected log-date window. While the feed loads, skeleton placeholders preserve the layout.

Selecting an event opens its detail sidebar, where the full record is available subject to your entitlements.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FRsg9n7HyOcDheHIiG6Se%2Fresim.png?alt=media&amp;token=0fe008ef-75fc-4ed3-8719-8ef52feab66e" alt=""><figcaption></figcaption></figure>

### Status and resolution

Events carry a status so they can be triaged. You can change an event's status as you work through the feed, and filter by status to focus on what remains open.

### Exporting

The feed can be exported to CSV under the current filters for offline reporting.


# Saved Incidents

Saved Incidents is a personal collection of records you have set aside for follow-up. Saving a record keeps it available for later review without re-running a search.

**Availability:** All plans.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FYgSbetP1xvv6sbq8xRjZ%2Fresim.png?alt=media&amp;token=e3c5ec64-3cff-41df-85f9-5b02b0b5933d" alt=""><figcaption></figcaption></figure>

### Saving a record

From a record's detail view, use the save control to add it to your Saved Incidents. The saved entry retains the key identifying fields so you can return to it directly.

### The table

The Saved Incidents table lists each saved record with:

* an identifier,
* the account,
* the application,
* the record type,
* the date it was saved,
* a classification,
* and per-row actions.

Long account and application values can be copied inline. On narrow viewports the table collapses into a stacked card per record so it remains readable.

### Actions

Each row provides:

* **View** — reopen the full record detail.
* **Delete** — remove the record from your saved collection.

Deleting a saved incident removes it from this list only; it does not affect the underlying record in the corpus.


# Threat Feeds

Threat Feeds is the live intelligence stream. It aggregates dark web activity, indicators of compromise, threat-actor profiles, and related reporting into a single, continuously updated surface.

**Availability:** Full access to Threat Feeds and its detail views requires a Threat Intelligence subscription. Lower tiers see the module with an upgrade prompt.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Fi1PDLPWtOspdHl0kAG0Q%2Fresim.png?alt=media&amp;token=00ee9c95-6e43-4edb-a785-f6613b8b5bc9" alt=""><figcaption></figcaption></figure>

### What it covers

Threat Feeds brings together several categories of intelligence:

* **Dark web chatter and mentions** — posts and discussions surfaced from monitored sources.
* **Indicators of compromise (IOCs)** — observed indicators with their technical context.
* **Threat actors** — profiles assembled for tracked actors.
* **Related reporting** — news and analysis tied to the above.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FcM6C1jZq2Wz04vOL8v6z%2Fresim.png?alt=media&amp;token=6d5e0051-5100-4d46-8cdf-fab6e7949ca8" alt=""><figcaption></figcaption></figure>

### Detail views

Selecting an item opens a detail sidebar appropriate to its type:

* Dark web chatter opens an intel detail view with the post content and, where available, screenshots in a lightbox.
* An IOC opens a technical detail view with its attributes, confidence, and associated context.
* A threat actor opens a profile view with the actor's status, first and last seen, and related findings.

These detail sidebars share a consistent layout and behavior with the rest of the platform.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F181Z9Ld3FkBtS2Tq4GbA%2Fresim.png?alt=media&amp;token=2ac34645-70db-4fcf-8c6c-528ea897de6d" alt=""><figcaption></figcaption></figure>

### Subscription notice

Because Threat Feeds content is part of the Threat Intelligence tier, detail requests verify entitlement. When access is not included, the platform presents a blurred preview and an upgrade prompt rather than the full content.


# Brand Protection

Brand Protection monitors for domains registered to impersonate your brand and manages the takedown process for them. It covers look-alike detection, per-domain investigation, and takedown request tracking.

**Availability:** Enterprise or Threat Intelligence subscription. Lower tiers see the module with an upgrade prompt.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FxSSxyQnsBAxBB1q6Gkh0%2Fresim.png?alt=media&amp;token=119b34db-6ffb-4604-ab94-203cc06ed204" alt=""><figcaption></figcaption></figure>

### Enabling detection

Look-alike detection runs against the domains on your watchlist. Enable **Detect look-alike domains** on a domain identifier in Watchlists to begin receiving detections. Detected domains then appear in the Brand Protection views.

### Look-alike views

Brand Protection presents two views in a sub-tab strip:

* **All Domains** — every detected look-alike, with the domain it impersonates, the detected domain, takedown state, a screenshot, HTTP status, MX presence, registrar, registration date, and detection date.
* **Takedown Requests** — the takedowns you have filed, with their status and history.

While a view loads, a column-matched skeleton table is shown.

### Per-domain detail

Selecting a detected domain opens a detail view with deeper technical context, including DNS, WHOIS, SSL, HTTP response, page title, redirect chain, and related signals, to support an assessment of intent.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FnbYtDh0EanyD6OEwDiVU%2Fresim.png?alt=media&amp;token=3c8282b9-9710-4748-a7db-a989fea1a0ac" alt=""><figcaption></figcaption></figure>

### Takedowns

You can request a takedown for a detected domain, and you can file an ad hoc takedown for a domain you discovered yourself. Takedowns consume takedown credits; the available balance is shown on the Takedown Requests view, with a top-up path when the balance is exhausted. The Takedown Requests table summarizes each request's status, type, last update, and filing date, and can be filtered by status.

### Exporting

The look-alike list can be exported to CSV with configurable scope, date range, and status.


# Supplier Security

Supplier Security extends WhiteIntel's monitoring to your third parties. It tracks the suppliers you depend on, scores their security posture, and surfaces events affecting them, so third-party risk is visible alongside your own exposure.

**Availability:** Enterprise or Threat Intelligence subscription. Lower tiers see the module with an upgrade prompt.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FbL0w9vJfYjfPDZaBbx8Z%2Fresim.png?alt=media&amp;token=11145245-9ba1-43fc-9cee-8aaa701ca9f3" alt=""><figcaption></figcaption></figure>

### The supplier list

The main view lists every monitored supplier with, for each:

* the supplier identity and domain,
* a letter grade,
* a numeric risk score, with an indicator when the score has moved,
* industry and country,
* the last event,
* the date last scored,
* and a monitoring status.

The list can be searched by domain or name, and sorted by name, score, most recent event, or last scored. On narrow viewports each supplier is presented as a self-contained card so suppliers remain easy to distinguish.

### Adding and managing suppliers

Suppliers are added and removed from the **Manage Suppliers** view, reachable from the page header. The tracked supplier list is maintained on the server, so it is consistent across sessions and users in your organization.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F7SRlVfIhKijbHDy35zb5%2Fresim.png?alt=media&amp;token=1ed54abe-c6a9-4ed9-a4b9-818bb1d7d915" alt=""><figcaption></figcaption></figure>

### Supplier detail

Selecting a supplier opens a dedicated detail page with the supplier's score breakdown, monitored signals, and the events affecting it, giving a full posture view for that third party.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F7MBIkaw8aix5XcwMo1nC%2Fresim.png?alt=media&amp;token=5b153258-70ae-415a-96d8-6a016043b22c" alt=""><figcaption></figcaption></figure>


# Payment Fraud Intelligence

Payment Fraud Intelligence surfaces compromised payment-card data relevant to your organization, so fraud and risk teams can identify exposed cards and act on them.

**Availability:** Tier-gated. The Overview is reachable on all plans; full card detail and analysis require the applicable subscription. Lower tiers see the module with an upgrade prompt.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FaJO4tl59IWfcm0GfzuYD%2Fresim.png?alt=media&amp;token=92884388-3f92-4590-91ea-08ebf098deb8" alt=""><figcaption></figcaption></figure>

### Data handling

Card data is presented in a privacy-preserving form. Card numbers are never shown in full: only the issuer identification digits and the last four digits are displayed, and security codes are never shown. This allows identification and matching of exposed cards without exposing usable card data.

### Card information

The card view lists exposed cards with their non-sensitive attributes, including the card network, the card tier, and the issuing context. Card networks such as Visa, Mastercard, and American Express are shown as labeled badges for quick scanning.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FpAxdi4O8fu1MWsdAQkDu%2Fresim.png?alt=media&amp;token=446d1957-d367-467a-a6d6-f3b4017e6e17" alt=""><figcaption></figcaption></figure>

### Card detail

Selecting a card opens a detail view with its available non-sensitive fields, including network, tier, and the associated context, formatted for review and case work.

### Filtering and search

The module supports filtering and search to narrow the card set to a specific network, tier, or other attribute, so you can focus on the cards relevant to a given investigation.


# CSV exports and export credits

Several modules can export their results as a CSV file for offline analysis, reporting, or ingestion into another system. Server-side exports are billed against export credits. This page explains where exports are available, who can run them, and the cost model.

**Availability:**

* **Single-domain export (Global Search)** — available on any subscription that has CSV export credits. Use it to export the results for a single domain.
* **Multi-domain export (Dashboard)** — exporting across a watchlist group through Your Dashboard, including the Endpoints and Credentials data sets, requires an Enterprise or Threat Intelligence subscription.

All server-side exports consume export credits, which are an organization-level resource.

### Export credits

Export credits are tracked at the organization level. Before an export, the export view shows your available balance, retrieved from the platform. The action is disabled when you have no remaining credits, or when your plan does not include the export you are attempting.

After an export completes, the balance is updated immediately and reconciled against the server, so the figure stays current without a manual refresh.

### Cost model

Cost is measured in valid domains exported:

* **Single domain** — one credit.
* **Watchlist group (multi-domain)** — one credit per valid domain in the group. Restricted domains and email-provider domains are skipped and are not charged.

The cost is stated before you confirm, shown as an exact figure for a single domain and as an upper bound for a group. An export that returns no rows still charges, because the cost is per domain, not per row.

### Single-domain export from Global Search

Any subscription that has export credits can export the results of a Global Search for a single domain. Run a search, then use the export control to download the matching records as a CSV file. This is the most direct path when you only need one domain's results, and it is not restricted to a particular tier.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FaqOWZ2qWLZ76qd8ojq2I%2Fresim.png?alt=media&amp;token=84fe1c6f-e051-46e1-8966-8f6f062af269" alt=""><figcaption></figcaption></figure>

### Dashboard exports (Endpoints and Credentials)

The Endpoints and Credentials tabs of Your Dashboard provide their own exports, including the ability to export an entire watchlist group in one operation. Because these support multi-domain export, they require an Enterprise or Threat Intelligence subscription; on lower tiers the export control is disabled and labeled accordingly.

#### Endpoint export

From the Endpoints tab, the export produces a CSV of the infected machines for the selected domain or group, with columns for hostname, source domain, country, operating system, IP, corporate record count, infection date, index date, device identifier, and system identifier. In group views you can scope the export to all domains or to a single member.

#### Record export

From the Credentials tab, the export produces a CSV of the raw records. You select the record type, a required date range, an optional source filter, and optional infected-system columns. The date range is bounded by your plan, and the platform reports a clear message if the requested range exceeds that bound.

### How exports are delivered

Exports stream as a file download. The file includes a header row and is named to reflect the scope and the time of export. On success, the export view reports the number of rows and the credits charged, and notes if a row cap was reached. On failure, the platform shows the specific reason, and any charge that could not be fulfilled is not applied.


# Webhooks

Webhooks deliver platform events to an external endpoint so you can integrate WhiteIntel detections into your own systems, such as a SIEM, a ticketing workflow, or a custom automation.

**Availability:** Threat Intelligence subscription. Lower tiers see the page with an upgrade prompt.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FJUdfId0KylWaNYIe9tFf%2Fresim.png?alt=media&amp;token=a1ffbdab-5985-4b80-b319-d00fae1a29d3" alt=""><figcaption></figcaption></figure>

### Configuring a webhook

The Webhooks page lets you register and manage the endpoint that receives event deliveries. Configuration is gated on your subscription; if your plan does not include webhooks, the page presents an upgrade path rather than the configuration form.

### Relationship to alerts

Webhooks complement the alert delivery options configured per identifier in Watchlists, such as Jira and Slack. Use per-identifier delivery for routing specific watchlist alerts, and webhooks for programmatic, system-to-system integration.


# API access

Whiteintel exposes a REST API so you can query the corpus and integrate intelligence into your own tooling. Programmatic access is authenticated with an API key.

**Availability:** API access depends on your plan. Where it is not included, the platform presents an upgrade path.

<div align="left"><figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FKCBMa7U5lGfvXdn2Qjxb%2Fresim.png?alt=media&amp;token=f7e3c87a-ea17-4dc2-a527-790e1920ab40" alt=""><figcaption></figcaption></figure></div>

### Your API key

Your API key is managed from the **Profile** or **Organizations** page, under the API key tab. The key is masked by default and can be revealed and copied. If your key may have been exposed, you can regenerate it; regenerating immediately invalidates the previous key, so update any integrations before doing so.

Some keys are inherited from your organization. In that case, the key is read-only for standard members, and only organization administrators can rotate it. See Organization settings.

### Reference documentation

The full API reference, including endpoints, parameters, and example requests, is published at the external API documentation site. It is linked from the navigation rail under[ **API Docs**.](https://docs.whiteintel.io/)

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Fb0CDvylbNoYw6RKHlAvd%2Fresim.png?alt=media&amp;token=2abd065c-da94-44c3-b488-2603357666b8" alt=""><figcaption></figcaption></figure>


# Microsoft SSO Configuration

WhiteIntel supports Microsoft Entra ID (Azure AD) single sign-on (SSO), allowing your team to securely log in using their corporate Microsoft accounts instead of managing separate passwords.

### Prerequisites

Before enabling Microsoft SSO, make sure you have:

* An **active WhiteIntel Enterprise or Threat Intel plan**
* **Admin access** to your organization in WhiteIntel
* **Admin access** to your Microsoft Entra ID (Azure AD) tenant

### Step 1 — Create an App Registration in Azure

1. Sign in to the Azure Portal
2. Navigate to **Azure Active Directory > App registrations**.
3. Click **New Registration**.
4. Fill in the following:
   1. **Name**: `WhiteIntel SSO` (or any descriptive name)
   2. **Supported account types**: *Accounts in this organizational directory only*
   3. **Redirect URI**: <https://platform.whiteintel.io/login>

### Step 2 — Gather Required Information

* Log in to the **WhiteIntel Dashboard** as an organization admin.
* Go to **Organization Settings > SSO Configuration**.
* Enter the values from Azure:
  * **Tenant ID**
  * **Client ID**
  * **Client Secret** *(create one for WhiteIntel if not exists)*
* Confirm the **Redirect / Callback URL** is exactly: <https://platform.whiteintel.io/login>

### Step 3 — Configure SSO in WhiteIntel

* Log in to the **WhiteIntel Dashboard** as an organization admin.
* Go to **Organization Settings > SSO Configuration**.
* Enter the values from Azure:
  * **Tenant ID**
  * **Client ID**
  * **Client Secret**&#x20;
* Optionally, toggle **Enforce SSO only** to disable password login for all users.


# Jira Configuration

WhiteIntel supports Jira integration, allowing your team to create autonomous and on-demand jira tickets.

### Prerequisites

* An **active WhiteIntel Enterprise or Threat Intel plan**
* **Admin access** to your organization in WhiteIntel
* **Admin access** to your Atlassian

### Step 1

1. Sign in to Atlassian
2. Go to Atlassian Account → Security → API tokens
3. Click **Create API token**.\
   Give it a descriptive name (e.g., “WhiteIntel Jira Integration”) and set an expiry if offered (typically 1–365 days).
4. Click **Create**, then **Copy** the token and store it securely (you won’t be able to view it again).

{% hint style="danger" %}

### We highly recommend creating a service account with limited privileges to only create Tickets. Do not directly use your Atlassian admin account API key.

{% endhint %}

### Step 2

* Log in to the **WhiteIntel Dashboard** as an organization admin.
* Go to **Organizations > Jira**
* Enable  configuration

### Step 3

* Go to Watchlists page on Whiteintel Dashboard
* Enable "Push to Jira" checkbox on the targets that you want to get alerted via Jira.

Additionaly, for on demand ticket creations, you can click the Jira icon on the top of the Details bar of incidents.


# Slack Configuration

WhiteIntel supports Slack integration, allowing your team to get alerted autonomous and on-demand via Slack messages.

### Prerequisites

* An **active WhiteIntel Enterprise or Threat Intel plan**
* **Admin access** to your organization in WhiteIntel
* **Admin access** to your Slack

### Step 1

1. Go to the Slack app manager and create a new app (From scratch)
2. In your app → **Features** → **Incoming Webhooks** → toggle **On**
3. Click **Add New Webhook to Workspace**, pick the target channel, then **Allow**. Slack will generate a unique **Webhook URL** for that channel
4. Copy the Webhook URL

### Step 2

* Log in to the **WhiteIntel Dashboard** as an organization admin.
* Go to **Organizations > Slack**
* Enable configuration

### Step 3

* Go to Watchlists page on Whiteintel Dashboard
* Enable "Push to Slack" checkbox on the targets that you want to get alerted via slack.

Additionaly, for on demand Slack message, you can click the Slack icon on the top of the Details bar of incidents.


# Profile and security

The Profile page is where you manage your own account: your password, two-factor authentication, active sessions, API key, and account deletion.

**Availability:** All plans.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FSRCS8EM2iODC6fZCjaVy%2Fresim.png?alt=media&amp;token=6676599a-2f5a-496c-9ce0-30ad5d3a2ead" alt=""><figcaption></figcaption></figure>

### Identity strip

A summary strip at the top of the page shows your email, your organization, your plan, your two-factor status, and your subscription expiry at a glance. While the page loads, a placeholder is shown so the card does not appear abruptly.

### Password

Update your password from the Password section. Use a strong, unique password; the form requires your current password and a confirmation of the new one.

### Two-factor authentication

Two-factor authentication delivers a one-time code by email on each sign-in. You can enable or disable it from the Two-factor authentication section, which requires your current password to make the change. The current state is shown as a status indicator.

### Sessions

The Sessions tab lists recent sign-ins with their date and IP address, so you can review where your account has been accessed.

### API key

The API key tab shows your key, masked by default, with reveal, copy, and, where permitted, regenerate controls. See API access.

### Deleting your account

The Danger zone provides account deletion. When you start a deletion, the platform performs a precheck: if you are the sole administrator of an organization, or if a deletion is otherwise not permitted, it explains why and directs you to the appropriate next step. Eligible deletions require your current password and an explicit typed confirmation, and the action is irreversible.


# Organization settings

Organization settings is the administration surface for organization accounts. From here, administrators manage members, single sign-on, the organization API key, and review the organization's license and entitlements.

**Availability:** Organization accounts. Some controls are restricted to organization administrators.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FMfxp8B1nFBPT6TJ3kENh%2Fresim.png?alt=media&amp;token=e6c9dc41-6b2f-4f3f-bdad-070cf0611bf6" alt=""><figcaption></figcaption></figure>

### Organization identity strip

A summary strip at the top shows which organization you are managing, its plan, seat usage, and expiry status. While the data loads, a placeholder is shown.

<div align="left"><figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FWuOy93ftA6jcDBZ8XXeV%2Fresim.png?alt=media&amp;token=0dda93ef-d484-4610-bca8-1eb42479f573" alt=""><figcaption></figcaption></figure></div>

### Users and roles

The Users panel lists organization members with their role. Administrators can invite new users and remove existing ones. Roles include an administrator role, which carries the management permissions described on this page. Invitations are subject to a daily limit, which the platform reports when reached.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Fik8E9Ngpok0uwV2g1HDL%2Fresim.png?alt=media&amp;token=d0c912bb-ddb8-49fe-b18f-8c761a5aa38d" alt=""><figcaption></figcaption></figure>

### License and entitlements

The License tab summarizes the organization's plan: name, plan type, expiry, seats used and total, CSV export limit, API limit, and the identifier quotas by type. This is the authoritative view of what the organization is entitled to.

### Single sign-on

Organizations can provision access through Microsoft Entra ID (Azure AD). The SSO tab captures the tenant and client configuration, supports verification, and allows enforcing SSO for the organization. The client secret is never prefilled.

<div align="left"><figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2Fu0DRoeSTpBZE8h8MahNg%2Fresim.png?alt=media&amp;token=e4a54806-3a45-4b2e-b50d-70fc835c82eb" alt=""><figcaption></figcaption></figure></div>

### Organization API key

The organization API key is managed here. Members may inherit this key; only administrators can rotate it. Rotating immediately invalidates the previous key, so update integrations beforehand. See API access.

### Integrations

Organization-level integration settings, such as Jira and Slack delivery used by watchlist alerts, are configured here so they are available to the whole organization.

<div align="left"><figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FdE5hYH0HAJkaS7Cm5Vj2%2Fresim.png?alt=media&amp;token=596ba264-e158-43d7-9e11-90835db8b72a" alt=""><figcaption></figcaption></figure></div>


# Dashboard

The dashboard provides detailed insights into data breaches associated with a searched domain. This information includes the total number of compromised devices, the total number of customer credentials stolen by information stealer malware, the total number of employee credentials, incident timelines, and the total number of customer and combolist exposures.

You can simply utilize the search bar on the header to give it a try.<br>

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F4rWjQdHNfaMrWwR4XYX8%2Fresim.png?alt=media&amp;token=49b19c70-d3d0-489c-86ad-321e457b9095" alt=""><figcaption></figcaption></figure>


# Global Search

The **Global Search** page is the central hub for querying our breach intelligence database. It allows users to perform targeted searches across **billions of leaked records** collected from stealer logs, combolist breaches, exposed infrastructure, and more.

With Global Search, you can:

* Search by **domain**, **subdomain**, **APK Package**, **email**, **IP address**, or **device hostname**
* Filter results by **record type**, **breach source**, or **date**
* Instantly view exposed credentials, associated applications, and breach context
* Export results to CSV for further analysis
* Unlock enriched insights with advanced filters (TI-only features)

Global Search is designed to surface relevant breach intelligence quickly, whether you're investigating a potential compromise, monitoring brand exposure, or conducting threat research.

> 📌 Tip: Access to certain filters and data types—such as IPs or computer names—requires an active **Threat Intelligence** license.

{% content-ref url="/pages/oQV612Glb8NgUpcSFMSt" %}
[Corporate Records](/basics/corporate-records)
{% endcontent-ref %}

{% content-ref url="/pages/YHtVkaJkKIOwEMxHU4m0" %}
[Consumer Records](/basics/consumer-records)
{% endcontent-ref %}

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FdASV0PO1qy9aNLojcmDk%2Fresim.png?alt=media&amp;token=bafd2406-a5ce-4343-a5e2-2eabec80d317" alt=""><figcaption></figcaption></figure>

After performing a search, you can **view the contents of a breach** by clicking the **"View"** button next to a result. If the item hasn't been unlocked yet, you'll be prompted to use one of your **unlock tokens** to access the full breach details.


# Watchlists

The **Watchlists** feature allows you to monitor specific assets for exposure in real-time. By adding domains, email addresses, IPs, device hostnames, GitHub repositories or keywords to your watchlist, Whiteintel will automatically alert you when these items appear in newly discovered breach data.

Watchlists help you:

* Proactively detect breaches tied to your organization or personal identifiers
* Receive **real-time alerts** when monitored assets are exposed
* Track activity across **domains, emails, IP addresses, hostnames, GitHub Repositories and keywords.**
* Prioritize incidents by relevance to your environment

> 🔐 Some watchlist types (such as IPs and hostnames) require a **Threat Intelligence** license for activation.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FO0ivbuWpph09XnJlX3oI%2Fresim.png?alt=media&amp;token=3666100f-3c2f-49e7-a279-1739adac5700" alt=""><figcaption></figcaption></figure>


# Watchlist Events

The **Watchlist Events** page displays real-time alerts for any item on your Watchlist that has been detected in breach data.

As WhiteIntel continuously scans new breach records, this page is automatically updated with events linked to your monitored **domains**, **emails**, **IP addresses**, or **hostnames**.

Each event includes:

* The **type of asset** that triggered the alert (e.g., domain, email, IP)
* The **event date** (when it was detected in our breach sources)
* The **breach type** (e.g., `stealer`, `combolist`)
* The **number of credentials or records** exposed
* A **“View” button** to dive deeper into the breach details

This page helps you:

* Monitor exposures relevant to your organization or research targets
* Stay up to date without manually searching
* Quickly investigate incidents as they happen

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FPV8FimrIcF4S4GJM8A5P%2Fresim.png?alt=media&amp;token=8a9116e8-5295-484d-aa88-a031d363bbb7" alt=""><figcaption></figcaption></figure>

> 📌 Tip: Watchlist Events are automatically generated and updated based on your active Watchlist items. You can control which items are tracked from the Watchlists page.


# Organization Settings

#### 🏢 Organization Settings

The **Organization Settings** page is where admins can manage users, roles, and license usage across their organization’s WhiteIntel account.

This page is especially useful for teams using **multi-seat subscriptions**, allowing for secure collaboration and centralized license management.

***

**👥 Manage Users**

Admins can:

* **View all users** within the organization
* See when each user was added
* **Invite new users** via email
* **Remove users** who no longer need access
* Assign roles (e.g., `admin`, `analyst`) to control permissions
* Enable / Disable Microsoft SSO

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FYxlTrCrhCHeGWAKwCiHS%2Fresim.png?alt=media&amp;token=9157b258-8e96-4fd9-9d75-d62d5f94204c" alt=""><figcaption></figcaption></figure>


# API Access

To retrieve or regenerate your API key, you can simply visit API section on Profile or Organization page.\
\
![](https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F4HT8TG09HVg8JlzdJqud%2Fresim.png?alt=media\&token=7bbac6ba-f8bb-4c5d-bdd0-a43a647d957a)

To have API Document please visit: <https://docs.whiteintel.io>


# Webhooks

The **Webhook Settings** section allows your organization to receive real-time alerts whenever watchlist items such as domains, IPs, emails, or hostnames are detected in new stealer logs.\
This feature is only available for Threat Intelligence licenses.\
\
To access detailed webhook document, please visit [WhiteIntel Webhook API](https://docs.whiteintel.io/whiteintel-api-doc/webhooks/whiteintel-webhook-api-incoming)\
\ <img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FPQWH9tA52Mpd9kJoatSJ%2Fresim.png?alt=media&amp;token=9385d0b0-ed49-4423-b1b2-ed9609edf0fa" alt="" data-size="original">


# Look-alike Domain Monitoring

WhiteIntel now includes **Look-alike Domain Monitoring,** a proactive detection system that identifies newly registered domains that visually or textually resemble your protected assets or brand names.

This feature helps organizations detect **impersonation**, **phishing**, and **brand abuse** attempts early, before they are weaponized.

***

### 🔍 Overview

When attackers register domains that closely mimic legitimate ones (e.g., `micros0ft-support.com` instead of `microsoft.com`), they often use them in phishing campaigns, credential harvesting, or malware delivery.

Whiteintel continuously scans newly registered domain names worldwide and identifies those similar to any domain on your **Watchlist**.

Detected domains are added as new **Watchlist Events** under the *Look-alike* category.

***

### 🧠 How It Works

1. **Continuous Monitoring**\
   New domain registrations are checked against your protected entries using fuzzy-matching algorithms (string similarity, homograph patterns, and brand resemblance).
2. **Automated Enrichment**\
   When available, WHOIS and DNS data are retrieved to help assess the legitimacy or potential risk of each detected domain.
3. **Event Generation**\
   When a match is found, a **Look-alike Event** is created within your Watchlist, grouped by the original monitored domain.
4. **Alert Delivery**\
   If configured, alerts are also sent via Slack and Jira integrations.

***

### 🧾 Event Details

Each Look-alike event includes:

* **Detected Domains:** The list of newly registered domains that resemble your monitored entry.
* **WHOIS & DNS Data (when available):** Registrar, creation/expiry dates, name servers, and abuse contact emails.

You can view these under the **Contents** tab in your event sidebar.\
If WHOIS data is unavailable for a domain, it will be marked as *No WHOIS available*.

***

### 💡 Example Use Case

* **Brand Protection:** Detect newly registered look-alike domains impersonating your organization or customers.
* **Phishing Prevention:** Identify domains that could be used in future email or website impersonation.
* **Threat Hunting:** Investigate registrar trends and ownership overlaps with known malicious actors.

***

### ⚙️ License Availability

Look-alike Domain Monitoring is available for:

* **Enterprise**
* **Threat Intelligence (TiFirm)**

Customers on these licenses automatically receive access to this feature.\
If you are on a Researcher plan and wish to upgrade, please contact support.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F1c6YWkiKksJiiYHIC9y2%2Fresim.png?alt=media&amp;token=2699c1a6-0b3c-4a3f-9f82-c9449f84843f" alt=""><figcaption></figcaption></figure>

***

***

### 💬 Support

If you have any questions or would like to enable this feature, contact us at:\
📧 <info@whiteintel.io>

***

> *Available to customers with active Enterprise or Threat Intelligence subscriptions.*


# Public GitHub Repository Scan (Beta)

### Overview

WhiteIntel’s **Public GitHub Repository Scan** feature helps detect **exposed secrets, credentials, and sensitive information** in public GitHub repositories.\
This extends your visibility beyond the dark web by monitoring open-source code bases for potential leaks that could compromise your organization or clients.

The scanner analyzes **all branches** and **complete commit history** of each repository to identify exposures early and reduce the risk of source code–based breaches.

> ⚠️ Currently available in **Beta** for Enterprise and Threat Intelligence license holders.

***

### Availability by License

| License Type            | Repositories Supported | Branch Coverage | Commit History | CSV Export | Integrations |
| ----------------------- | ---------------------- | --------------- | -------------- | ---------- | ------------ |
| **Enterprise**          | Up to 8 repositories   | All branches    | Full history   | Yes        | Jira, Slack  |
| **Threat Intelligence** | Up to 16 repositories  | All branches    | Full history   | Yes        | Jira, Slack, |

***

### How It Works

Once enabled, WhiteIntel connects to our GitHub scanning engine and performs a full inspection of the selected repositories:

1. **Crawls all branches and commit history** for the specified public repository
2. **Applies secret-detection rules** (API keys, tokens, credentials, configuration leaks, etc.)
3. **Correlates findings** with WhiteIntel’s threat intelligence pipeline
4. Displays the results in your dashboard and provides CSV export for further analysis

> Each finding includes:
>
> * Repository name and branch
> * File path and affected lines
> * Commit hash, author, and timestamp
> * Detected rule ID and matched pattern
> * Secrets

***

### How to Use

#### Access

1. Log in to your WhiteIntel dashboard.
2. Go to **Watchlists → GitHub Repository type**.
3. Click **Add Identifier**.
4. Enter the public repository URL (e.g., `https://github.com/organization/repo-name.git`).
5. Confirm to start scanning.

#### Viewing Results

* Scan results appear under the **Watchlist Events** section with file paths, commit metadata, and matched secret patterns.
* You can export the results as a CSV file by clicking **Download CSV** in the sidebar.
* Results are updated periodically as new commits are detected.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FOErGIZaO0vbCC69UMlvO%2Fresim.png?alt=media&amp;token=315facb4-8f8a-48cd-9d02-ea3c0303c498" alt=""><figcaption></figcaption></figure>

***


# Investigations+ (Beta)

Investigation+ is WhiteIntel’s premium forensic suite, designed to transform raw log data into actionable intelligence. By leveraging neural correlation and autonomous heuristics, this module allows analysts to de-anonymize targets, visualize lateral exposure, and prioritize critical assets through a centralized dashboard experience.

> ⚠️ Platform Availability: This module is accessible exclusively through the WhiteIntel Web Dashboard. To protect the integrity of our identity graph and the compute-heavy neural models involved, this feature is not available via the  API.

### 🚀 Core Capabilities

The Investigation+ module is built around four pillars of forensic discovery:

## 1. Comprehensive Assets Discovery

The Investigation+ module provides a comprehensive inventory of all known assets connected to the target username or email. This view consolidates fragmented log data into a unified forensic profile.

### 1.1. Connected Assets

The engine aggregates and displays:

* Computer Names: Hostnames of every infected machine linked to the target.
* IP Addresses: History of connection points and network origins.
* Observed Countries: Geographic anchoring based on IP telemetry and TLD analysis.
* Related Accounts: Secondary usernames, aliases, and emails used by the same individual.
* Passwords: A curated list of observed passwords, useful for identifying credential reuse patterns.

#### 1.2. Application Intelligence

The Results Tab also features a Detailed List of Affected Applications, showing every service, portal, or software package where the target's credentials have been captured.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FMyRmJ9bbhDs6oS12DlIg%2Fimage.png?alt=media&amp;token=346f9125-4fb3-42ad-be63-793b70831c23" alt=""><figcaption></figcaption></figure>

## 2. Neural Identity Resolution

The engine performs linguistic forensics across thousands of data points to extract real-world identities from digital aliases.

* Cultural Anchoring: Matches surname patterns with detected geographic anchors (e.g., matching Pinyin names with `.gov.cn` assets).
* Cross-Log Correlation: Aggregates identifiers from multiple infected systems to build a single "Primary Identity" profile.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F9stYdc6eral8ASvhtdkS%2Fimage.png?alt=media&amp;token=9c96ea8d-fa2d-4045-9040-51d5892549fa" alt=""><figcaption></figcaption></figure>

## 3. Forensic Graph Reconstruction

Visualize how a threat actor or target moves across a network. The graph maps the relationship between Infected Systems, Related Accounts, and Applications.

* Interactive Expansion: Click nodes to perform "Deep Dives" into secondary pivots.
* Application Nodes: Identify specific services where credentials were exfiltrated.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2F76Q8F1TQx6YfC0Q0MVvT%2Fimage.png?alt=media&amp;token=f64262db-8694-416c-9e6b-1534c1707abb" alt=""><figcaption></figcaption></figure>

## 4. Smart Credential Prioritization

Instead of manually sorting through thousands of rows, the system automatically flags credentials based on their institutional value.

* High-Value Tags: Automatic categorization of Gov, Edu, and Malicious (Underground Forum) logins.
* Risk Context: Prioritizes administrative access and internal infrastructure portals.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FN0L8KesAOJTjF7uHPNQk%2Fimage.png?alt=media&amp;token=ecd12d2e-12b2-48af-af09-753ccf2a23a1" alt=""><figcaption></figcaption></figure>

## 5. Automated Risk Scoring

Every investigation is assigned a Risk Index based on the severity of the exposed data.

* Critical: Access to Government infrastructure or active presence on Tier-1 malicious forums.
* Elevated: Access to corporate VPNs, Cloud management panels, or financial portals.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FbBOyyEBoDafwhkH6EuJZ%2Fimage.png?alt=media&amp;token=51454028-5a15-492e-b915-4477aafb8c69" alt=""><figcaption></figcaption></figure>

### 🛠 Using the Module

There are two primary ways to initiate a Neural Investigation. Currently, investigations are supported for usernames and email addresses.

#### Method A: The Investigations Tab

Users can navigate directly to the Investigations tab to manage existing cases or start a new manual lookup for a specific target identity.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FxwZ6DShhdE2JNU5Fzjpf%2Fimage.png?alt=media&amp;token=3ca23815-1607-4ed6-938c-6dae496bbd44" alt=""><figcaption></figcaption></figure>

#### Method B: Global Search Integration

When using the Global Search bar, the system will provide an indication if an AI Analysis is available for a given entry. This allows for a seamless transition from a general search to a deep forensic dive.

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FYuyPD8UknYAFdr7nXbfF%2Fimage.png?alt=media&amp;token=ea8c4ed2-35bf-405e-9009-57a1d8ca85cc" alt=""><figcaption></figcaption></figure>

<figure><img src="https://1828548938-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fw17PvzOvioV4AGBNsfYd%2Fuploads%2FJvTabyPyaATWBiPqaZ4V%2Fimage.png?alt=media&amp;token=8ab3550d-6d30-401e-b49d-a0ef2438d1a8" alt=""><figcaption></figcaption></figure>

### 💳 Licensing & Access

Investigation+ is a premium feature requiring specific entitlements:

* Threat Intel License: Included by default for all users on the Threat Intel (tifirm) plan.
* Researcher/Enterprise Licenses: Available as an add-on for $1,500 USD / year.

To upgrade your access or purchase the add-on, please visit the Upgrades section in your dashboard settings.

[whiteintel.io](https://whiteintel.io)


# Researcher Subscription

Researcher subscription is perfect for individual cybersecurity experts, bug bounty hunters, and enthusiasts.

License includes:

* &#x20;500 data unlocks a month
* &#x20;Domain, subdomain, email address based searches
* &#x20;Watchlist feature for Domains
* &#x20;Real-time alerts
* &#x20;1 seat

Current accepted payment methods are:&#x20;

* Master Card, Visa Card, Amex, Paypal

In order to obtain a researcher license please contact us at  <sales@whiteintel.io>

{% hint style="danger" %}
Due to the sensitive and potentially high-impact nature of the intelligence we provide, WhiteIntel requires all customers to undergo a **manual Know Your Customer (KYC)** process prior to license activation.

This process ensures that access is granted only to verified individuals or organizations with proven ethical intent. Our data is strictly for white-hat security research, corporate defense, and responsible usage.

For the **Researcher** license, applicants are required to submit:

* Links to social or professional profiles (e.g., LinkedIn, GitHub, Twitter)
* Bug bounty platform accounts (e.g., HackerOne, Bugcrowd), if available
* A short statement about intended use
* A government-issued ID may be requested for identity verification

For **Enterprise** and **Threat Intelligence** licenses, we additionally verify organizational identity, domain ownership, and employee affiliation.

WhiteIntel reserves the right to deny or revoke access if the applicant’s intent cannot be confidently verified as ethical or compliant with our terms of use.
{% endhint %}


# Enterprise Subscription

Enterprise license is tailored for organizations needing scalable access with advanced export and automation support.

Enterprise license includes:

&#x20;   • Unlimited data unlocks\
&#x20;   • Domain, subdomain, email based searches\
&#x20;   • Watchlist feature for Domains\
&#x20;   • Email address watchlist\
&#x20;   • 10 CSV exports / day\
&#x20;   • 50 API calls / day\
&#x20;   • Real-time alerts\
&#x20;   • 2 seats

### **Pricing**

Current pricing for Threat Intel Subscription is 400 USD / Month or 4000 USD / year (additional taxes may be included)

Current accepted payment methods are:&#x20;

* Master Card, Visa Card, Amex, Paypal, Master Card, Visa Card, Amex, Paypal, Wire Transfer

In order to obtain Enterprise license, please contact us at <info@whiteintel.io>

{% hint style="danger" %}
Due to the sensitive and potentially high-impact nature of the intelligence we provide, WhiteIntel requires all customers to undergo a **manual Know Your Customer (KYC)** process prior to license activation.

This process ensures that access is granted only to verified individuals or organizations with proven ethical intent. Our data is strictly for white-hat security research, corporate defense, and responsible usage.

For the **Researcher** license, applicants are required to submit:

* Links to social or professional profiles (e.g., LinkedIn, GitHub, Twitter)
* Bug bounty platform accounts (e.g., HackerOne, Bugcrowd), if available
* A short statement about intended use
* A government-issued ID may be requested for identity verification

For **Enterprise** and **Threat Intelligence** licenses, we additionally verify organizational identity, domain ownership, and employee affiliation.

WhiteIntel reserves the right to deny or revoke access if the applicant’s intent cannot be confidently verified as ethical or compliant with our terms of use.

***

{% endhint %}


# Threat Intel Subscription

Threat Intel license is designed for SOCs and threat intel teams requiring high-volume data access and integration.

Current TI Firm subscription includes:

&#x20;   • Unlimited data unlocks\
&#x20;   • Domain, subdomain, email, IP, and computer name based searches\
&#x20;   • Watchlist feature for: Email, IP, Computer name values\
&#x20;   • 500 CSV exports / day\
&#x20;   • 500 API calls / day\
&#x20;   • Real-time alerts\
&#x20;   • Only this license permits resale or embedding of WhiteIntel data in customer-facing products\
&#x20;   • 3 seats

### **Pricing**

Current pricing for Threat Intel Subscription is 750 USD / Month or 7500 USD / year (additional taxes may be included)

Current accepted payment methods are:&#x20;

* Master Card, Visa Card, Amex, Paypal, Wire Transfer

In order to obtain Enterprise license, please contact us at <info@whiteintel.io>

{% hint style="danger" %}
Due to the sensitive and potentially high-impact nature of the intelligence we provide, WhiteIntel requires all customers to undergo a **manual Know Your Customer (KYC)** process prior to license activation.

This process ensures that access is granted only to verified individuals or organizations with proven ethical intent. Our data is strictly for white-hat security research, corporate defense, and responsible usage.

For the **Researcher** license, applicants are required to submit:

* Links to social or professional profiles (e.g., LinkedIn, GitHub, Twitter)
* Bug bounty platform accounts (e.g., HackerOne, Bugcrowd), if available
* A short statement about intended use
* A government-issued ID may be requested for identity verification

For **Enterprise** and **Threat Intelligence** licenses, we additionally verify organizational identity, domain ownership, and employee affiliation.

WhiteIntel reserves the right to deny or revoke access if the applicant’s intent cannot be confidently verified as ethical or compliant with our terms of use.
{% endhint %}

To obtain a TI Firm license, please contact us at <info@whiteintel.io> or utilize the contact form in the web page <https://whiteintel.io/contact>


# FAQ

Ever since we have founded the WhiteIntel platform, these are the questions we get asked a lot by our customers. So we've decided to make a comprehensive list of common questions about our platform and answer them. Please do not hesitate to contact us at <info@whiteintel.io> if you have any further questions, we are always here to help!\
\
Q: **How does WhiteIntel work?**\
A: WhiteIntel continuously searches threat intelligence resources and acts as a database, indexing any and all recent infostealer logs and combolists shared by threat actors.

\
Q: **What type of data leak sources does WhiteIntel monitor?**\
A: WhiteIntel monitors both public and private telegram groups, discord channels, surface-web and dark-web forums and many other places for infostealer logs and combolists.<br>

Q: **How does real-time alerting work?**\
A: WhiteIntel automatically ingests and indexes newly published infostealer logs and combolists. Based on the customer Watchlist rules, once a new information leak is identified customers are immediately alerted.<br>

Q: **How frequently does your threat intelligence database update?**\
A: WhiteIntel database is updated on a 24/7 basis. This process is automated and as soon as a new leak is detected, it is uploaded to our database.<br>

Q: **Can I integrate WhiteIntel to my product via API ?**\
A: Threat Intelligence license allows you to integrate WhiteIntel logs to your product via API and developer support is provided upon request.<br>

Q: **Can I provide service to my clients via WhiteIntel ?** \
A: Yes, Threat Intelligence license allows cybersecurity companies to share data to their respective customers.<br>

Q: **Are Credentials on this platform unique?**\
A: No. If an infostealer log is available on WhiteIntel, it means threat actors also have access to it.<br>

Q: **Can I request a Proof of Concept?**\
A: Yes! Please reach out to <info@whiteintel.io><br>

Q: **Can I pay with crypto currencies?**\
A: No. Our company’s country of residence does not allow us to receive payments with crypto currencies.<br>

Q: **Why do you need KYC ?**\
A: Due to the sensitive nature of intelligence provided, WhiteIntel has to conduct due diligence and make sure only authorized and reputable cybersecurity professionals have access to our platform.<br>

Q: **Can my or my client’s unmasked credentials be accessed on this platform?**\
A: No. Company verification and KYC is required. However, since our logs are compiled and indexed from threat sources, chances are other people have already access to the credentials.<br>

Q: **What is the legality of this service?**\
A: WhiteIntel acts as a database indexing service for infostealer and combolist leaks and we are not the primary source of the credentials provided. WhiteIntel strictly abides by the local laws and regulations concerning cybersecurity. Here is a fun read on the topic from NATO: <https://ccdcoe.org/uploads/2020/05/CyCon_2020_4_Nweke_Wolthusen.pdf><br>

Q: **Are you validating credentials?**\
A: No, this would not be possible due to the legality of the service. We can not access third party applications. It is up to the customers to validate and conduct incident response to the reported credentials.<br>

Q: **Infostealer log shows incorrect date / a date in the future, is your platform broken?**\
A: No, WhiteIntel acts as a database index, therefore incorrect dates are a result of incorrect time settings on the infected computer.<br>

Q: **What is the difference between Infostealer leaks and Combolist leaks?**

* Infostealer leaks : Infostealers are a type of malware that steals the usernames, emails and passwords that are stored within web browsers and sometimes password managers upon infecting victim computers.
* Combolist leaks : Combolists are compiled from previous database breaches and infostealer logs and generally used with OpenBullet to infiltrate target web applications with username:password combination.

Q: **Your platform has this credential but other platforms do not have it, what gives?**\
A: Each threat intelligence platform has common and private log sources, so it is up to the customer to evaluate the best possible intelligence source. It is natural that some log types and credentials will show up in one platform but will not in the other.<br>

Q: **XYZ platform has this credential, but you don’t?**\
A: WhiteIntel, we do our best to provide the most recent data leaks as quickly as possible so our customers can take preventative measures. For example, our platform is not concerned about some database leak from 2019 where an ex-employee has had a password leak.\
\
WhiteIntel ensures the information provided is actionable intelligence from most recent and up-to-date leaks, so older breaches may not show up on our platform.\
&#x20;